Basic iptables Rulesets for IPv4 and IPv6
19/04/2024
Comments off
 Appropriate firewall rules heavily depend on the services being run. Below are iptables rulesets to secure your Linode if you’re running a web server. These are given as an example! A real production web server may want or require more or less configuration and these rules would not be appropriate for a file or database server, Minecraft or VPN server, etc.
iptables rules can always be modified or reset later, but these basic rulesets serve only as a beginning demonstration.
IPv4
- /tmp/v4
-
*filter

# Allow all loopback (lo0) traffic and reject traffic
# to localhost that does not originate from lo0.
-A INPUT -i lo -j ACCEPT
-A INPUT ! -i lo -s 127.0.0.0/8 -j REJECT

# Allow ping and traceroute.
-A INPUT -p icmp --icmp-type 3 -j ACCEPT
-A INPUT -p icmp --icmp-type 8 -j ACCEPT
-A INPUT -p icmp --icmp-type 11 -j ACCEPT

# Allow SSH connections.
-A INPUT -p tcp -m state --state NEW --dport 22 -j ACCEPT

# Allow HTTP and HTTPS connections from anywhere
# (the normal ports for web servers).
-A INPUT -p tcp --dport 80 -j ACCEPT
-A INPUT -p tcp --dport 443 -j ACCEPT

# Accept inbound traffic from established connections.
-A INPUT -m state --state ESTABLISHED,RELATED -j ACCEPT

# Log what was incoming but denied (optional but useful).
-A INPUT -m limit --limit 5/min -j LOG --log-prefix "iptables_INPUT_denied: " --log-level 7

# Reject all other inbound.
-A INPUT -j REJECT

# Log any traffic which was sent to you
# for forwarding (optional but useful).
-A FORWARD -m limit --limit 5/min -j LOG --log-prefix "iptables_FORWARD_denied: " --log-level 7

# Reject all traffic forwarding.
-A FORWARD -j REJECT

COMMIT


Optional: If you plan to use Linode Longview, add this additional rule below the section for allowing HTTP and HTTPS connections:
# Allow incoming Longview connections
-A INPUT -s longview.linode.com -m state --state NEW -j ACCEPT
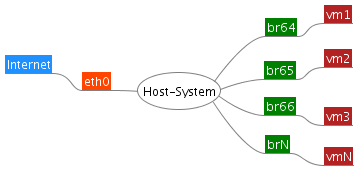 IPTables is responsible to handle packet filtering in Linux system. IPTables contains several predefined and/or user-defined tables. Each table contains chains and chain contain packet rules. IPTables uses NAT table to forward packets to another node.