Archive

Archives pour la catégorie ‘Réseau’

Automatically Connect to a Network Drive on Mac OS X Start Up & Login

02/01/2024 Comments off

It can be helpful to configure Mac OS X to automatically mount shared network drives, this is particularly true for those of us who regularly connect to a network drive for file sharing or backups.

Setting up automatic network drive connections in OS X is a two-step process, you must mount the drive, then you add it to your automatic login items. This should work flawlessly in most versions of OS X, but we’ll cover an alternative approach that uses Automator to mount a network drive automatically on login as well.

1) Mounting the Network Drive

If you’re already familiar with mapping a network drive in Mac OS X you can skip the first part of this and go straight to System Preferences in the second section.

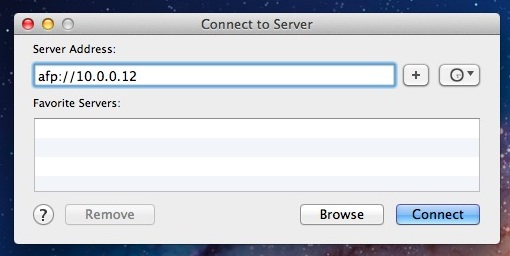
  1. From the OS X desktop, pull down the “Go” menu and select “Connect to Server”
  2. Connect to the server and mount the drive you want to automatically connect to on boot
  3. Choose Guest or for a specific user check the box next to “Remember this password in my keychain” – you must select to remember the password otherwise the automatic login event can not happen without logging into the network drive

Next, you add the network drive to automatically connect on OS X by bringing it into your Login Items list.

Lire la suite…

Categories: Réseau, Système Tags: , ,

Configuration avancée du firewall iptables

01/01/2024 Comments off

Iptables c’est quoi ?

Iptables est un firewall pour les distributions linux. Wikipédia et d’autres articles expliquent ça bien mieux que moi, du coup je ne vais pas m’attarder là dessus. Mais pour faire simple, un pare-feu système est un logiciel qui vient contrôler les flux réseaux connectés avec votre machine. Conceptuellement, le firewall va recevoir les flux réseaux, avant la socket. Il va alors appliquer différentes règles sur ce dernier, en fonction des résultats des tests par rapport à ces règles, un firewall laissera passer la connexion vers la socket ou rejettera le flux.

Les firewalls sont indispensables de nos jours en sécurité informatique, il s’agit souvent de la 1ère ligne de défense d’une machine connectée sur internet et dans le cas de réseau d’entreprise, un des éléments vraiment efficace pour limiter les rebonds d’un attaquant dans votre réseau.

Bref, les firewalls c’est bon mangez-en…

Mettre à jour Iptables en 1.6.1

Alors sur une debian 8, c’est la version 1.4.1 qui était présente sur mon serveur. J’ai profité de ce TP pour la mettre à jour vers la dernière version. Les sources officielles sont disponibles sur le site du projet :

https://www.netfilter.org/projects/iptables/index.html

Et voici comment mettre à jour votre firewall.

Dépendances

Quelques paquets sont nécessaires à la dernière version, certains sont présents dans les dépots debian :

apt-get install libbison-dev, flex

D’autres non, et sont à télécharger et installer depuis netfilter.org .

libmnl

curl -O https://www.netfilter.org/projects/libmnl/files/libmnl-1.0.4.tar.bz2
tar xvf libmnl-1.0.4.tar.bz2
cd libmnl-1.0.4/
./configure && make
make install
cd ..
rm -Rf libmnl-1.0.4*

libnftnl

curl -O https://www.netfilter.org/projects/libnftnl/files/libnftnl-1.0.8.tar.bz2
tar xvf libnftnl-1.0.8.tar.bz2
cd libnftnl-1.0.8/
./configure && make
make install
cd ..
rm -Rf libnftnl-1.0.8*

Mettre à jour iptables 1.6.1

curl -O https://www.netfilter.org/projects/iptables/files/iptables-1.6.1.tar.bz2
tar xvf iptables-1.6.1.tar.bz2
cd iptables-1.6.1
./configure && make
make install

Je vous recommande un petit reboot, suite à l’installation comme on touche à des modules kernel.

shutdown -r now

Et vous pourrez alors vérifier que la dernière version d’iptables est bien installée à l’aide de la commande :

# iptables -V
iptables v1.6.1

Pour les N00bs, quelques règles simples

Conceptuellement, iptables fonctionne avec des « tables » et des « chains« . Si vous débutez avec iptables , considérez qu’il n’existe qu’une table de règles : « filter » dans la chaîne « INPUT« , et ne vous occupez pas (encore) du reste. Et vous devez simplement vous dire qu’un paquet TCP à destination de votre serveur va être analysé par chaque règle présente dans cette table de votre firewall pour décider s’il est accepté ou rejeter. On reviendra sur les autres tables dans la partie configuration avancée du firewall iptables plus tard dans ce tutoriel.

Le b.a.-ba d’un pare-feu c’est « d’ouvrir et de fermer » des ports TCP. Comprendre, autoriser des connexions sur certains ports TCP et les refuser sur les autres.

Lire la suite…
How To Use Apache JMeter To Perform Load Testing on a Web Server

30/12/2023 Comments off

Introduction

In this tutorial, we will go over how to use Apache JMeter to perform basic load and stress testing on your web application environment. We will show you how to use the graphical user interface to build a test plan and to run tests against a web server.

JMeter is an open source desktop Java application that is designed to load test and measure performance. It can be used to simulate loads of various scenarios and output performance data in several ways, including CSV and XML files, and graphs. Because it is 100% Java, it is available on every OS that supports Java 6 or later.


Prerequisites

In order to follow this tutorial, you will need to have a computer that you can run JMeter on, and a web server to load test against. Do not run these tests against your production servers unless you know they can handle the load, or you may negatively impact your server’s performance.

You may adapt the tests in this tutorial to any of your own web applications. The web server that we are testing against as an example is a 1 CPU / 512 MB VPS running WordPress on a LEMP Stack, in the NYC2 DigitalOcean Datacenter. The JMeter computer is running in the DigitalOcean office in NYC (which is related to the latency of our tests).

Please note that the JMeter test results can be skewed by a variety of factors, including the system resources (CPU and RAM) available to JMeter and the network between JMeter and the web server being tested. The size of the load that JMeter can generate without skewing the results can be increased by running the tests in the non-graphical mode or by distributing the load generation to multiple JMeter servers.  Lire la suite…

Linux: 20 Iptables Examples For New SysAdmins

23/12/2023 Comments off

According to the official project site:

netfilter is a set of hooks inside the Linux kernel that allows kernel modules to register callback functions with the network stack. A registered callback function is then called back for every packet that traverses the respective hook within the network stack.

This Linux based firewall is controlled by the program called iptables to handles filtering for IPv4, and ip6tables handles filtering for IPv6. I strongly recommend that you first read our quick tutorial that explains how to configure a host-based firewall called Netfilter (iptables) under CentOS / RHEL / Fedora / Redhat Enterprise Linux. This post lists most simple iptables solutions required by a new Linux user to secure his or her Linux operating system from intruders. Lire la suite…

Top 32 Nmap Command Examples For Sys/Network Admins

22/12/2023 Comments off

The purpose of this post is to introduce a user to the nmap command line tool to scan a host and/or network, so to find out the possible vulnerable points in the hosts. You will also learn how to use Nmap for offensive and defensive purposes.

nmap in actionnmap in action

More about nmap

From the man page:

Nmap (“Network Mapper”) is an open source tool for network exploration and security auditing. It was designed to rapidly scan large networks, although it works fine against single hosts. Nmap uses raw IP packets in novel ways to determine what hosts are available on the network, what services (application name and version) those hosts are offering, what operating systems (and OS versions) they are running, what type of packet filters/firewalls are in use, and dozens of other characteristics. While Nmap is commonly used for security audits, many systems and network administrators find it useful for routine tasks such as network inventory, managing service upgrade schedules, and monitoring host or service uptime.

It was originally written by Gordon Lyon and it can answer the following questions easily:

  1. What computers did you find running on the local network?
  2. What IP addresses did you find running on the local network?
  3. What is the operating system of your target machine?
  4. Find out what ports are open on the machine that you just scanned?
  5. Find out if the system is infected with malware or virus.
  6. Search for unauthorized servers or network service on your network.
  7. Find and remove computers which don’t meet the organization’s minimum level of security.

Lire la suite…

Categories: Réseau, Système Tags: