Archive

Archives pour la catégorie ‘Logiciel’

How to monitor a Linux server and desktop remotely from web browser

21/11/2023 Comments off

Monitoring Linux server

When it comes to monitoring a Linux server, there are more than enough options to choose from. While there are many production-quality monitoring solutions (e.g., Nagios, Zabbix, Zenoss), boasting of fancy UI, monitoring scalability, comprehensive reporting capabilities, etc., these solutions are probably an overkill for most of us end users. If all you need is to check the basic status (e.g., CPU load, memory usage, active processes, disk usage) of a remote Linux server or desktop, consider linux-dash.

linux-dash is a web-based lightweight monitoring dashboard for Linux machines, which can display, in real-time, various system properties, such as CPU load, RAM usage, disk usage, Internet speed, network connections, RX/TX bandwidth, logged-in users, running processes etc. linux-dash does not come with any backend database for storing long-term statistics. Simply drop in linux-dash app in an existing web server (e.g., Apache, Nginx), and you are good to go. It is a quick and easy way to set up remote monitoring for personal projects.

In this tutorial, I am going to describe how to set up linux-dash in Nginx web server on Linux. Nginx is preferred over Apache web server due to its lightweight engine.

Set up linux-dash on Debian, Ubuntu or Linux Mint

First, install Nginx web server with php-fpm.

$ sudo apt-get install git nginx php5-json php5-fpm php5-curl

Configure Nginx for linux-dash app by creating /etc/nginx/conf.d/linuxdash.conf as follows. In this example, we are going to use port 8080.

$ sudo vi /etc/nginx/conf.d/linuxdash.conf
server {
 server_name $domain_name;
 listen 8080;
 root /var/www;
 index index.html index.php;
 access_log /var/log/nginx/access.log;
 error_log /var/log/nginx/error.log;
 
 location ~* .(?:xml|ogg|mp3|mp4|ogv|svg|svgz|eot|otf|woff|ttf|css|js|jpg|jpeg|gif|png|ico)$ {
 try_files $uri =404;
 expires max;
 access_log off;
 add_header Pragma public;
 add_header Cache-Control "public, must-revalidate, proxy-revalidate";
 }
 
 location /linux-dash {
 index index.html index.php;
 }
 
 # PHP-FPM via sockets
 location ~ .php(/|$) {
 fastcgi_param SCRIPT_FILENAME $document_root$fastcgi_script_name;
 fastcgi_split_path_info ^(. ?.php)(/.*)$;
 fastcgi_pass unix:/var/run/php5-fpm.sock;
 if (!-f $document_root$fastcgi_script_name) {
 return 404;
 }
 try_files $uri $uri/ /index.php?$args;
 include fastcgi_params;
 }
}

Disable the default site configuration.

$ sudo rm /etc/nginx/sites-enabled/default

Configure php-fpm by editing /etc/php5/fpm/pool.d/www.conf. Make sure to edit « user« , « group » and « listen » directives as shown below. You can keep the rest of the configuration unchanged.

$ sudo vi /etc/php5/fpm/pool.d/www.conf

. . .
user = www-data
group = www-data
listen = /var/run/php5-fpm.sock
. . .

Proceed to download and install linux-dash.

$ git clone https://github.com/afaqurk/linux-dash.git
$ sudo cp -r linux-dash/ /var/www/
$ sudo chown -R www-data:www-data /var/www

Restart Nginx web server as well as php5-fpm to finalize installation.

$ sudo service php5-fpm restart
$ sudo service nginx restart
Lire la suite…

Phishing: Un développeur web recommande l’utilisation de « rel=noopener »

18/11/2023 Comments off

Pour empêcher les attaques par hameçonnage lancées en se servant du window.opener

phishingEn HTML, l’attribut “rel” peut être utilisé sur les balises <a> (qui permet de créer un lien hypertexte pointant vers un document en spécifiant l’URL de celui-ci au niveau de l’attribut « href” et qui permet également de définir des ancres au sein d’un document et les liens pour y accéder), <area> (qui permet de définir une zone particulière d’une image et peut lui associer un lien hypertexte) et <link> (qui permet de définir l’emplacement d’un fichier qui sera accessible au sein de la page où elle est déclarée couramment utilisée pour mettre en relation d’autres documents comme les feuilles de style).

Dans ces différentes balises, il est utilisé pour détailler la relation existante entre le document courant et le document qui sera ouvert par le lien et il prend pour valeur des éléments d’une liste de différentes relations dont les valeurs sont séparées par des virgules (par exemple “alternate”, “author”, “bookmark”, “help”, “license”, “next”, “nofollow”, “noreferrer”, “prefetch”, “prev”, “search”, “tag”).

Mathias Bynens, un développeur web front-end dans la ville de Termonde en Belgique, a voulu partager avec la communauté des développeurs web les bienfaits de l’une des valeurs de l’attribut “rel”, notamment “noreferrer” qui permet entre autres de résoudre un problème, mais lequel ?

En guise de démonstration, dans un billet blog il a proposé une petite expérience. Bynens propose les URL index.html et index/malicious.html. En définissant un lien vers la seconde URL avec l’attribut “target” qui avec la valeur “_blank”, cela va déclencher l’ouverture de la page cible dans une nouvelle fenêtre (dans ce cas la page malicious.html). Pour rappel, lorsqu’une fenêtre est ouverte depuis une autre fenêtre, elle conserve une référence à cette première fenêtre dans window.opener. Si la fenêtre courante n’a pas été ouverte par une autre fenêtre, la méthode renvoie null.

Bynens note que « le document malicious.html dans cette nouvelle page a l’élément windows.opener qui pointe vers l’élément window du document que vous regardez actuellement, c’est-à-dire index.html. Ce qui signifie que lorsque l’utilisateur clique sur le lien, malicious.html a un contrôle total sur l’objet window du document ». Dans le cas d’espèce, malicious.html vient remplacer l’onglet contenant index.html par index.html#hax, qui affiche un message caché.

« Ceci est un exemple relativement inoffensif, mais le lien aurait pu rediriger vers une page d’hameçonnage conçue pour ressembler à la vraie page index.html, demandant des informations de connexion. L’utilisateur ne l’aurait probablement pas remarqué, parce que l’accent est mis sur la page malveillante dans la nouvelle fenêtre tandis que la redirection se passe en arrière-plan. Cette attaque pourrait être encore plus subtile en ajoutant un retard avant de rediriger vers la page de phishing en arrière-plan », a-t-il avancé.

Dans cet exemple, index.html et index/malicious.html ont la même origine. Mais Bynens a indiqué qu’il est possible d’effectuer la même attaque avec des origines différentes.

Que faire pour empêcher que les pages n’abusent de window.opener ? Bynens recommande simplement de se servir de “rel=noopener”, « cela va permettre de vous assurer que window.opener a la valeur “null” sur Chrome 49 et Opera 36. Pour les navigateurs plus anciens, vous pouvez vous servir de “rel=noopener” qui va également désactiver l’en-tête HTTP “Refer”, ou alors vous servir de ce script JavaScript qui va potentiellement activer le bloqueur de popup.

var otherWindow = window.open();
otherWindow.opener = null;
otherWindow.location = URL;
Ne vous servez pas de “target=_blank” (ou tout autre “target” qui ouvre un nouveau contexte de navigation) en particulier pour les liens dans le contenu généré par l’utilisateur, à moins que vous n’ayez une bonne raison ».

Il a déjà averti les éditeurs de navigateurs dans des rapports de bogues. Le problème semble corrigé du côté de Chrome et Opera, mais pas encore chez Firefox, Safari et Edge.

Source : billet Mathias Bynens

Categories: Logiciel Tags: , ,

Owncloud: Using the occ Command

17/11/2023 Comments off

occ: la commande d’administration de ownCloud

ownCloud’s occ command

[ ATTRIBUTE: Please check: http://www.flickr.com/photos/91795203@N02/23828677959 to find out how to attribute this image]

owncloud
ownCloud’s occ command (ownCloud console) is ownCloud’s command-line interface. You can perform many common server operations with occ:

* Manage apps
* Manage users
* Convert the ownCloud database
* Reset passwords, including administrator passwords
* Convert the ownCloud database from SQLite to a more performant DB
* Query and change LDAP settings

occ is in the owncloud/ directory; for example /var/www/owncloud on Ubuntu Linux. occ is a PHP script. You must run it as your HTTP user to ensure that the correct permissions are maintained on your ownCloud files and directories.

The HTTP user is different on the various Linux distributions. See the Setting Strong Directory Permissions section of Installation Wizard to learn how to find your HTTP user.

  • The HTTP user and group in Debian/Ubuntu is www-data.
  • The HTTP user and group in Fedora/CentOS is apache.
  • The HTTP user and group in Arch Linux is http.
  • The HTTP user in openSUSE is wwwrun, and the HTTP group is www.

Running it with no options lists all commands and options, like this example on Ubuntu:

$ sudo -u www-data php occ
ownCloud version 8.0.3
Usage:
 [options] command [arguments]

Options:
 --help (-h)           Display this help message
 --quiet (-q)          Do not output any message
 --verbose (-v|vv|vvv) Increase the verbosity of messages: 1 for normal
                       output, 2 for more verbose output and 3 for debug
 --version (-V)        Display this application version
 --ansi                Force ANSI output
 --no-ansi             Disable ANSI output
 --no-interaction (-n) Do not ask any interactive question

Available commands:
 check                       check dependencies of the server environment
 help                        Displays help for a command
 list                        Lists commands
 status                      show some status information
 upgrade                     run upgrade routines after installation of a new
                             release. The release has to be installed before.

This is the same as sudo -u www-data php occ list.

Run it with the -h option for syntax help:

$ sudo -u www-data php occ -h

Display your ownCloud version:

$ sudo -u www-data php occ -V
  ownCloud version 8.0.3

Query your ownCloud server status:

$ sudo -u www-data php occ status
  - installed: true
  - version: 8.0.3.4
  - versionstring: 8.0.3
  - edition: Enterprise

occ has options, commands, and arguments. Options and arguments are optional, while commands are required. The syntax is:

occ [options] command [arguments]

Get detailed information on individual commands with the help command, like this example for the maintenance:mode command:

$ sudo -u www-data php occ help maintenance:mode
  Usage:
  maintenance:mode [--on] [--off]

  Options:
  --on                  enable maintenance mode
  --off                 disable maintenance mode
  --help (-h)           Display this help message.
  --quiet (-q)          Do not output any message.
  --verbose (-v|vv|vvv) Increase the verbosity of messages: 1 for normal
  output, 2 for more verbose output and 3 for debug
  --version (-V)        Display this application version.
  --ansi                Force ANSI output.
  --no-ansi             Disable ANSI output.
  --no-interaction (-n) Do not ask any interactive question.


Apps Commands

The app commands list, enable, and disable apps. This lists all of your installed apps, and shows whether they are enabled or disabled:

$ sudo -u www-data php occ app:list

Enable an app:

$ sudo -u www-data php occ app:enable external
  external enabled

Disable an app:

$ sudo -u www-data php occ app:disable external
  external disabled
Categories: Logiciel Tags:

13 Apache Web Server Security and Hardening Tips

15/11/2023 Comments off

Apache-Security-Tips1We all are very familiar with Apache web server, it is a very popular web server to host your web files or your website on the web. Here are some links which can help you to configure Apache web server on your Linux box.

Here in this tutorial, I’ll cover some main tips to secure your web server. Before you apply these changes in your web server, you should have some basics of the Apache server.

  • Document root Directory: /var/www/html or /var/www
  • Main Configuration file: /etc/httpd/conf/httpd.conf (RHEL/CentOS/Fedora) and /etc/apache/apache2.conf(Debian/Ubuntu).
  • Default HTTP Port: 80 TCP
  • Default HTTPS Port: 443 TCP
  • Test your Configuration file settings and syntax: httpd -t
  • Access Log files of Web Server: /var/log/httpd/access_log
  • Error Log files of Web Server: /var/log/httpd/error_log

1. How to hide Apache Version and OS Identity from Errors

When you install Apache with source or any other package installers like yum, it displays the version of your Apache web server installed on your server with the Operating system name of your server in Errors. It also shows the information about Apache modules installed in your server.

Show-Apache-Version

Show-Apache-Version

In above picture, you can see that Apache is showing its version with the OS installed in your server. This can be a major security threat to your web server as well as your Linux box too. To prevent Apache to not to display these information to the world, we need to make some changes in Apache main configuration file.

Open configuration file with vim editor and search for “ServerSignature“, its by default On. We need to Off these server signature and the second line “ServerTokens Prod” tells Apache to return only Apache as product in the server response header on the every page request, It suppress the OS, major and minor version info.

# vim /etc/httpd/conf/httpd.conf (RHEL/CentOS/Fedora)
# vim /etc/apache/apache2.conf (Debian/Ubuntu)
ServerSignature Off
ServerTokens Prod
# service httpd restart (RHEL/CentOS/Fedora)
# service apache2 restart (Debian/Ubuntu)
 

Hide-Apache-Version

2. Disable Directory Listing

By default Apache list all the content of Document root directory in the absence of index file. Please see the image below.

Apache-Directory-Listing

Apache-Directory-Listing

We can turn off directory listing by using Options directive in configuration file for a specific directory. For that we need to make an entry in httpd.conf or apache2.conf file.
<Directory /var/www/html>
    Options -Indexes
</Directory>
Hide-Apache-Directory-Listing

Hide-Apache-Directory-Listing

Lire la suite…

Categories: Logiciel, Sécurité Tags: , ,

How to turn off server signature on Apache2 web server

14/11/2023 Comments off

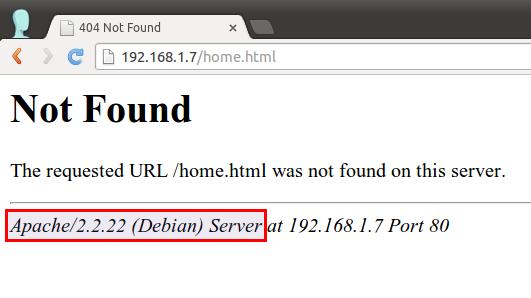
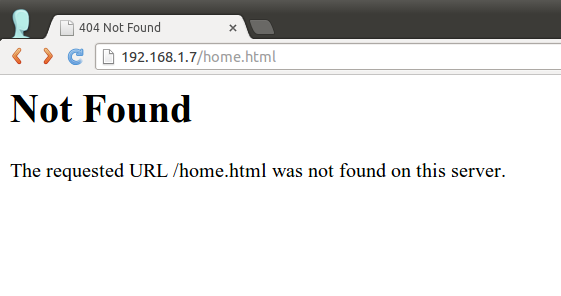
Question: Whenever Apache2 web server returns error pages (e.g., 404 not found, 403 access forbidden pages), it shows web server signature (e.g., Apache version number and operating system info) at the bottom of the pages. Also, when Apache2 web server serves any PHP pages, it reveals PHP version info. How can I turn off these web server signatures in Apache2 web server?

Revealing web server signature with server/PHP version info can be a security risk as you are essentially telling attackers known vulnerabilities of your system. Thus it is recommended you disable all web server signatures as part of server hardening process.

14902970545_c3d406322f_o14879982016_7c7b8bbf3d_o

Disable Apache Web Server Signature

Disabling Apache web server signature can be achieved by editing Apache config file.

On Debian, Ubuntu or Linux Mint:

$ sudo vi /etc/apache2/apache2.conf

On CentOS, Fedora, RHEL or Arch Linux:

$ sudo vi /etc/httpd/conf/httpd.conf

Add the following two lines at the end of Apache config file.

ServerSignature Off
ServerTokens Prod

Then restart web server to activate the change:

$ sudo service apache2 restart (Debian, Ubuntu or Linux Mint)
$ sudo service httpd restart (CentOS/RHEL 6)
$ sudo systemctl restart httpd.service (Fedora, CentOS/RHEL 7, Arch Linux)

The first line ‘ServerSignature Off‘ makes Apache2 web server hide Apache version info on any error pages.

14879982016_7c7b8bbf3d_o

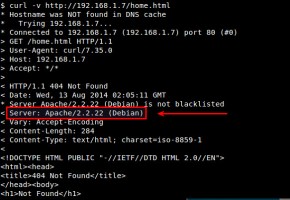
However, without the second line ‘ServerTokens Prod‘, Apache server will still include a detailed server token in HTTP response headers, which reveals Apache version number.

14902970535_e84ec23090_z

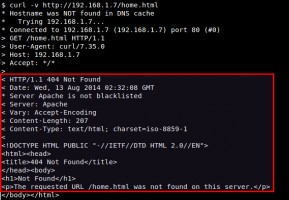
What the second line ‘ServerTokens Prod‘ does is to suppress a server token in HTTP response headers to a bare minimal.

So with both lines in place, Apache will not reveal Apache version info in either web pages or HTTP response headers.

14902970505_d79225f25d_z

Hide PHP Version

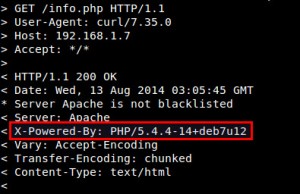
Another potential security threat is PHP version info leak in HTTP response headers. By default, Apache web server includes PHP version info via « X-Powered-By » field in HTTP response headers. If you want to hide PHP version in HTTP headers, open php.ini file with a text editor, look for « expose_php = On », and change it to « expose_php = Off ».

14899917981_aaef71eb0a

On Debian, Ubuntu, or Linux Mint:

$ sudo vi /etc/php5/apache2/php.ini

On CentOS, Fedora, RHEL or Arch Linux:

$ sudo vi /etc/php.ini

expose_php = Off

Finally, restart Apache2 web server to reload updated PHP config file.

Now you will no longer see « X-Powered-By » field in HTTP response headers.

Source: Xmodulo

Categories: Logiciel, Sécurité Tags: , ,