Archive

Articles taggués ‘iptables’

Contrer une attaque DDoS de type SYN flood sous Linux

15/05/2024 Comments off

Source: Tux-planet 

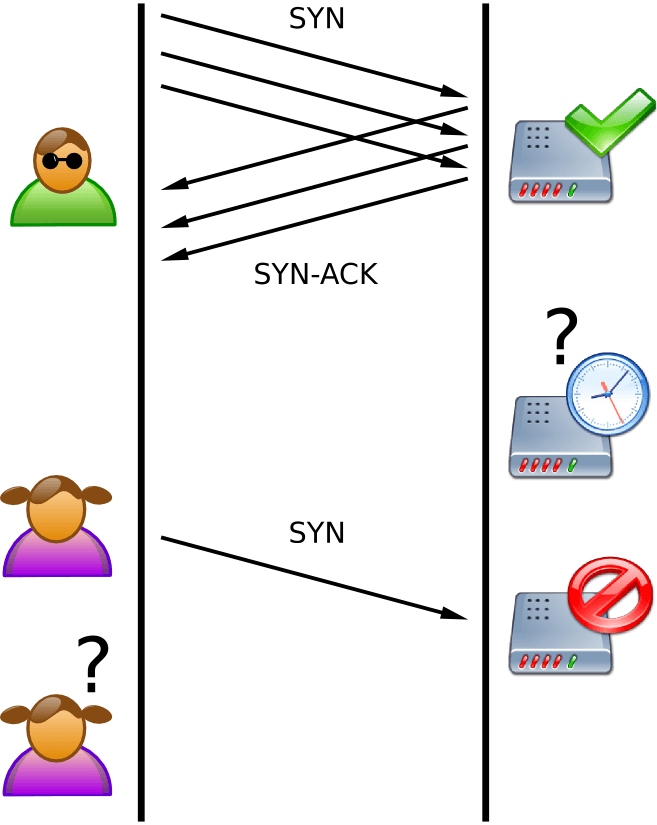
Une attaque par déni de services SYN flood est une technique visant à saturer un serveur en envoyant une multitude de paquets TCP, avec le flag SYN. Les connexions sont alors établies vers la machine, mais restent à moitié ouvertes, car le client malveillant (hacker) ne renvoie pas de confirmation (ACK).

Le serveur attend pendant un certain délai la réponse et la connexion semi-ouverte consomme alors un certain nombre de ressources. En multipliant ce type de connexions, le hacker peut arriver à créer un déni de service qui rendra la machine inopérante.

1. Détection d’une l’attaque DDoS SYN flood

Pour détecter la présence de l’attaque, il faut utiliser la commande netstat et repérer la présence des connexions de type SYN_RECV. Si il y a beaucoup de réponses, c’est qu’une attaque est sans doute en cours :

# netstat -an | grep SYN_RECV
 tcp 0 0 10.xxx.xxx.xxx 237.177.154.8:25882 SYN_RECV -
 tcp 0 0 10.xxx.xxx.xxx 236.15.133.204:2577 SYN_RECV -
 tcp 0 0 10.xxx.xxx.xxx 127.160.6.129:51748 SYN_RECV -
 tcp 0 0 10.xxx.xxx.xxx 230.220.13.25:47393 SYN_RECV -

Voici une autre commande, un peu plus sophistiquée, qui donnera de meilleures résultats quant à la détection d’une attaque DDoS :

for i in ` netstat -tanpu | grep "SYN_RECV" | awk {'print $5'} | cut -f 1 -d ":" | sort | uniq -c | sort -n | awk {'if ($1 > 3) print $2'}` ; do echo $i; done

Lire la suite…

Categories: Réseau, Sécurité Tags: , , ,

Use a load-balancer as a first row of defense against DDoS

14/05/2024 Comments off

Source: haproxy.com

We’ve seen recently more and more DOS and DDoS attacks. Some of them were very big, requiring thousands of computers…
But in most cases, this kind of attacks are made by a few computers aiming to make a service or website unavailable, either by sending it too many requests or by taking all its available resources, preventing regular users to use the service.
Some attacks targets known vulnerabilities of widely used applications.

In the present article, we’ll explain how to take advantage of an application delivery controller to protect your website and application against DoS, DDoS and vulnerability scans.

Why using a LB for such protection since a firewall and a Web Application Firewall (aka WAF) could already do the job?
Well, the Firewall is not aware of the application layer but would be useful to pretect against SYN flood attacks. That’s why we saw recently application layer firewalls: Web Application Firewalls, also known as WAF.
Well, since the load balancer is in front of the platform, it can be a good partner for the WAF, filtering out 99% of the attacks, which are managed by script kiddies. The WAF can then happily clean up the remaining attacks.
Well, maybe you don’t need a WAF and you want to take advantage of your Aloha and save some money ;).

Note that you need an application layer load-balancer, like Aloha or OpenSource HAProxy to be efficient.

TCP syn flood attacks

The syn flood attacks consist in sending as many TCP syn packets as possible to a single server trying to saturate it or at least, saturating its uplink bandwith.

If you’re using the Aloha load-balancer, you’re already protected against this kind of attacks: the Aloha includes mechanism to protect you.
The TCP syn flood attack mitigation capacity may vary depending on your Aloha box.

It you’re running your own LB based on HAProxy or HAPEE, you should have a look at the sysctl below (edit /etc/sysctl.conf or play with sysctl command):

# Protection SYN flood
 net.ipv4.tcp_syncookies = 1
 net.ipv4.conf.all.rp_filter = 1
 net.ipv4.tcp_max_syn_backlog = 1024

Note: If the attack is very big and saturates your internet bandwith, the only solution is to ask your internet access provider to null route the attackers IPs on its core network.

Lire la suite…

Analyser le réseau et filtrer le trafic avec un pare-feu

12/05/2024 Comments off

Source: OpenClassrooms

Ce chapitre vous propose d’apprendre à maîtriser le trafic réseau qui passe par votre ordinateur. En effet, lorsque vous êtes connectés à l’internet, vous avez régulièrement des applications qui vont se connecter puis télécharger et envoyer des informations. Comment surveiller ce qui se passe ? Quelle application est en train de communiquer et sur quel port ?

Savoir paramétrer un pare-feu est essentiel, que ce soit sur votre PC à la maison ou, à plus forte raison, sur un serveur. Cela vous protège de manière efficace contre les programmes qui voudraient échanger des informations sur le réseau sans votre accord. C’est une mesure de sécurité essentielle qu’il faut connaître et dont aucun administrateur système sérieux ne peut se passer. ;)

Je vous propose de découvrir d’abord quelques outils de base qui vont vous permettre de bien comprendre comment une IP est associée à un nom d’hôte. Puis nous analyserons le trafic en cours avec un outil comme netstat. Enfin — et ce ne sera pas le plus facile, je vous préviens — nous apprivoiserons le célèbre pare-feu utilisé sous Linux : iptables. Il est assez complexe à paramétrer, mais heureusement des programmes supplémentaires peuvent nous simplifier le travail.

host & whois : qui êtes-vous ?

Comme vous le savez sûrement, chaque ordinateur relié à l’internet est identifié par une adresse IP (figure suivante).

Une adresse IP est une suite de quatre nombres séparés par des points. Par exemple :86.172.120.28.

Categories: Réseau, Sécurité Tags: ,

Linux Iptables To Block Different Attacks

09/05/2024 Comments off

Source: linoxide.com

Iptables is a Linux kernel based packet filter firewall. The iptables modules are present in the kernel itself, there is no separate daemon for it. This makes it very fast and effective firewall. The iptables rules control the incoming and outgoing traffic on a network device. In this article, we will discuss about some common network attacks, and how we can block them using iptables. Some of the common network attacks are SYN flood attack, smurf attack, land attack, attacks by malfunctioning ICMP packet, and some other forms of DOS attack. Before going into the details of these attacks, let’s have an overview of iptables, and how to use this command.

Iptables

iptables has 3 filtering points for the default table: INPUT, OUTPUT and FORWARD. These are called chains in iptables. As their names suggest, they specify whether a packets is destined for the system (INPUT), originating from it (OUTPUT) or is routed to another node in the network (FORWARD).
The rules in iptables are stored in the form of records in a table. To list the rules, run “iptables -L”

root@local:~# iptables -L
 Chain INPUT (policy ACCEPT)
 target prot opt source destination

 Chain FORWARD (policy ACCEPT)
 target prot opt source destination

 Chain OUTPUT (policy ACCEPT)
 target prot opt source destination

Here, no rules are present for any chain.These rules are read from top to bottom, and if a match occurs, no further rules are checked. So if one rule overwrites any previous rule, then it must be below that rule. So we will append the rules below existing rules. But if your requirement is to insert explicitly, then you can insert them as well.

To insert a rule (above all other rules or at a specified number), -i, and to append, -A option is used. We need to specify the chain, for which we wish to write the rule. The -j option specifies the target, i.e. what we want to do with the packet if a rule is matched. Some of the values are ACCEPT, DROP (or REJECT), RETURN etc. This target can be some other existing or user defined chain. But for the purpose of this article, we will confine ourselves to existing chains only, and will not go in further details.

Lire la suite…

What Is SYN Flood Attack? Detection & Prevention In Linux

09/05/2024 Comments off

Source: linoxide.com

A SYN flood attack is a form of denial-of-service attack in which an attacker sends a large number of SYN requests to a target system’s services that uses TCP protocol. This will consume the server resources to make the system unresponsive to legitimate traffic. This attack can occur on any services that use TCP protocol and mainly on web service. In this article, we will go through the basics of SYN flood attacks and the mitigation steps in detail.

The SYN Flood attack exploits an implementation characteristic of the Transmission Control Protocol (TCP), which is called 3-way handshake. Following are the steps that happen in a normal 3-way handshake.

1. The client requests a connection by sending a SYN (synchronize) message to the server.
2. The server acknowledges this request by sending SYN-ACK back to the client.
3. The client responds with an ACK, and the connection is established

tcp_synflood

A SYN flood attack works by not responding to the server with the expected ACK code. By these half-open connections, the target machines TCP backlog will get filled up and hence all new connections may get ignored. This will cause the legitimate users will also get ignored.

Lire la suite…