Archive

Articles taggués ‘firewall’

Les Firewalls

09/08/2021 Comments off

par Alban Jacquemin et Adrien Mercier

1 – Pourquoi un firewall

De nos jours, toutes les entreprises possédant un réseau local possèdent aussi un accès à Internet, afin d’accéder à la manne d’information disponible sur le réseau des réseaux, et de pouvoir communiquer avec l’extérieur. Cette ouverture vers l’extérieur est indispensable… et dangereuse en même temps. Ouvrir l’entreprise vers le monde signifie aussi laisser place ouverte aux étrangers pour essayer de pénétrer le réseau local de l’entreprise, et y accomplir des actions douteuses, parfois gratuites, de destruction, vol d’informations confidentielles, … Les mobiles sont nombreux et dangereux.

Pour parer à ces attaques, une architecture sécurisée est nécessaire. Pour cela, le coeur d’une tel architecture est basé sur un firewall. Cette outil a pour but de sécuriser au maximum le réseau local de l’entreprise, de détecter les tentatives d’intrusion et d’y parer au mieux possible. Cela représente une sécurité supplémentaire rendant le réseau ouvert sur Internet beaucoup plus sûr.  De plus, il peut permettre de restreindre l’accès interne vers l’extérieur. En effet, des employés peuvent s’adonner à des activités que l’entreprise ne cautionne pas, le meilleur exemple étant le jeu en ligne. En plaçant un firewall limitant ou interdisant l’accès à ces services, l’entreprise peut donc avoir un contrôle sur les activités se déroulant dans son enceinte.

Le firewall propose donc un véritable contrôle sur le trafic réseau de l’entreprise. Il permet d’analyser, de sécuriser et de gérer le trafic réseau, et ainsi d’utiliser le réseau de la façon pour laquelle il a été prévu et sans l’encombrer avec des activités inutiles, et d’empêcher une personne sans autorisation d’accéder à ce réseau de données.

2 – Les différents types de filtrages

2.1 – Le filtrage simple de paquet (Stateless)

2.1.1 – Le principe

C’est la méthode de filtrage la plus simple, elle opère au niveau de la couche réseau et transport du modèle Osi. La plupart des routeurs d’aujourd’hui permettent d’effectuer du filtrage simple de paquet. Cela consiste à accorder ou refuser le passage de paquet d’un réseau à un autre en se basant sur :

– L’adresse IP Source/Destination.
– Le numéro de port Source/Destination.
– Et bien sur le protocole de niveau 3 ou 4.

Cela nécessite de configurer le Firewall ou le routeur par des règles de filtrages, généralement appelées des ACL (Access Control Lists).

2.1.2 – Les limites

Le premier problème vient du fait que l’administrateur réseau est rapidement contraint à autoriser un trop grand nombre d’accès, pour que le Firewall offre une réelle protection. Par exemple, pour autoriser les connexions à Internet à partir du réseau privé, l’administrateur devra accepter toutes les connexions TCP provenant de l’Internet avec un port supérieur à 1024. Ce qui laisse beaucoup de choix à un éventuel pirate.

Il est à noter que de définir des ACL sur des routeurs haut de gamme – c’est à dire, supportant un débit important – n’est pas sans répercussion sur le débit lui-même. Enfin, ce type de filtrage ne résiste pas à certaines attaques de type IP Spoofing / IP Flooding, la mutilation de paquet, ou encore certaines attaques de type DoS. Ceci est vrai sauf dans le cadre des routeurs fonctionnant en mode distribué. Ceci permettant de gérer les Acl directement sur les interfaces sans remonter à la carte de traitement central. Les performances impactées par les Acl sont alors quasi nulles.
Lire la suite…

Control Network Traffic with iptables

24/07/2021 Comments off

Packet filtering using network rules such as NAT (network address translation) can be accomplished by using iptables. Iptables utilize ports and protocols and may also be used as a firewall.

Using iptables for IPv4

By default, the iptables tool is included with your Linode supplied distribution. In order to use iptables, you will have to have root privileges to make changes. The location of the iptables files is in the /sbin directory. However, you will make changes to these files by invoking commands, not with a text editor.

The iptables Command

There are a number of options that can be used with iptables. Before you begin, you need to understand how iptables work. As stated above, iptables are used to set the rules governing network traffic. You can define different tables to handle these rules. The table contains a variety of built-in chains, but you can add your own chains. A chain is a list of rules that match a set of packets.

Basic iptables Parameters

In order to start using iptables, you will need to understand some basics about the command syntax. For example:

iptables -I INPUT -s 12.34.56.78 -j DROP

In the sample above you are invoking iptables by its name. The -I option is for insertion. Using a rule with the insertion option will add it at the beginning of a chain, it will also be the rule that is applied first. You may also use a number with -I option to indicate its placement in the chain. The -s parameter along with the IP address (12.34.56.78) indicates the source. Finally the -j parameter is for jump. It specifies the target of the rule i.e. what action it is to perform if the packet is a match.

For example, the rule above is added to the beginning of the chain, and it will drop all packets from the address 12.34.56.78 received from anywhere.

Parameter Description
-p, -- protocol The rule, such as TCP, UDP, etc.
-s, -- source Can be an address, network name, hostname, etc.
-d, -- destination An address, hostname, network name, etc.
-j, -- jump Specifies the target of the rule; i.e. what to do if the packet matches.
-g, --goto chain Specifies that the processing will continue in a user specified chain.
-i, --in-interface Names the interface from where packets are received.
-o, --out-interface Name of the interface by which a packet is being sent.
-f, --fragment The rule will only be applied to the second and further fragments of fragmented packets.
-c, --set-counters Enables the admin to initialize the packet and byte counters of a rule.

Default Tables

A root or sudo user can create tables. Tables are comprised of built-in chains and may also contain user-defined chains. The built-in tables present will depend on the kernel configuration and the installed modules. Below is a list of the tables available.

The default tables are as follows:

  • Filter – this is the default table. Its built-in chains are:
    • Input – is for packets going to local sockets
    • Forward – is for packets routed through the server
    • Output – is for locally-generated packets
  • Nat – when a packet creates a new connection this is the table that is used. Its built-in chains are Prerouting, Output, and Postrouting
    • Prerouting is for packets when they come in
    • Output is for locally-generated packets before routing takes place
    • Postrouting is for altering packets on the way out
  • Mangle – is used for special altering of packets. Its chains are Pre/Post routing, Forward, Input, and Output
    • Prerouting is for incoming packets
    • Postrouting is for packets going out
    • Output is for locally generated packets that are being altered.
    • Input is for packets coming directly into the server
    • Forward is for packets being routed through the server
  • Raw – is used primarily for configuring exemptions from connection tracking. The built-in chains are Prerouting and Output.
    • Prerouting is for packets that arrive by the network interface
    • Output is for processes that are locally generated
  • Security – is used for Mandatory Access Control (MAC) rules. After the filter table, the security table is accessed next. The built-in chains are Input, Output, and Forward.
    • Input pertains to packets entering the server
    • Output is for locally-generated packets
    • Forward is for packet passing through the server

Lire la suite…

How to Protect Successfully your network against DDoS attacks: 5 steps

15/07/2021 Comments off

Every business needs DDoS protection.

protect ddos attacksToday it’s important for the success of your business to have an online presence. You always thought that you would never be a victim of DDoS attacks. But, what would happen if your website or online application is down because of a DDoS attack?
Here are some facts taken from digitalattackmap:

  • Attacks are cheaper (150$ for a week long DDoS)
  • Their number are increasing every weeks (2000/day)
  • Increase attributed downtime (1/3 of all downtime incidents)

You can even block a 1TB DDoS attack!

With enough preparation, anybody can block a DDoS attack of any size and we will tell you how in 5 steps.

  1. Become invisible
  2. Filter aggressively
  3. Identify attack patterns
  4. Block traffic patterns
  5. Deploy counter-measures solutions

Lire la suite…

How To Isolate Servers Within A Private Network Using Iptables

05/07/2021 Comments off

Source: DigitalOcean – Mitchell Anicas

Introduction

In this tutorial, we will teach you how to use a Iptables with shared private networking to simulate the network traffic isolation that a true private network can provide. We will also cover why you would want to do this, and provide an example of how to implement this in your own environment. The example should explain the concept well enough that you should be able to adapt the configuration to your own needs.

DigitalOcean’s private networking option grants a second networking interface to a VPS, which is only accessible to other VPSs in the same datacenter–which includes the VPSs of other customers in the same datacenter. This is known as shared private networking. This means that data sent over a VPS’s private interface does not leave the datacenter at all, and no billable bandwidth usage will be incurred.

At the time of this writing, DigitalOcean offers the private networking option for VPSs in the following data centers:

  • Amsterdam 2
  • New York 2
  • Singapore 1

Note: This tutorial covers IPv4 security. In Linux, IPv6 security is maintained separately from IPv4. For example, iptables only maintains firewall rules for IPv4 addresses but it has an IPv6 counterpart called ip6tables, which can be used to maintain firewall rules for IPv6 network addresses.

If your VPS is configured for IPv6, please remember to secure both your IPv4 and IPv6 network interfaces with the appropriate tools. For more information about IPv6 tools, refer to this guide: How To Configure Tools to Use IPv6 on a Linux VPS

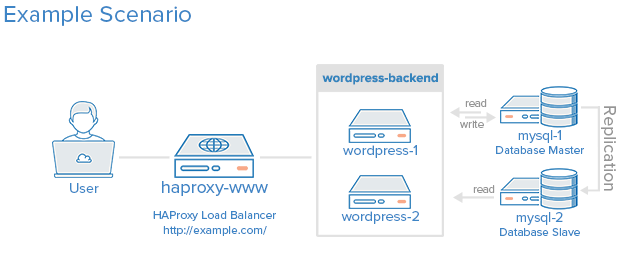
Example Scenario

For our example, we will use the environment created by the following tutorial: How To Optimize WordPress Performance With MySQL Replication On Ubuntu 14.04.

Here is a diagram of what the environment looks like:

prereq_no_private

The example environment uses five VPSs (and iptables are not configured):

  • haproxy-www: Reverse proxy load balancer
  • wordpress-1: First application server
  • wordpress-2: Second application server
  • mysql-1: Master MySQL database server
  • mysql-2: Slave MySQL database server

If your setup doesn’t look like this, you should still be able to follow along. Also, if you would like to read up on setting up a VPS with private networking or iptables basics, here are a few links that you might find to be useful (this tutorial assumes you know the basics of iptables):

If you are already familiar with the concepts, and would like to see the iptables setup, feel free to skip to the Overview of Iptables Configuration section.

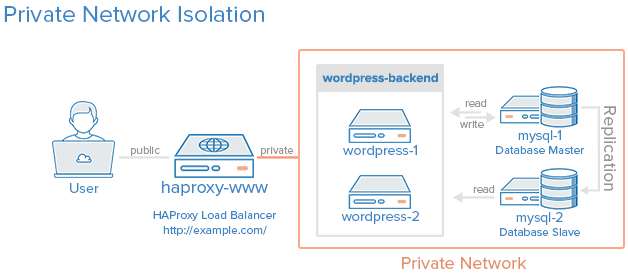
Our Goal

When we are finished with this tutorial, we should have an environment that looks something like the following diagram:

goal

All of the servers in the private network area can only be communicated with by other servers within this private network (the orange box). The load balancer will be accessible via the Internet and also be linked to the private network. The enforcement of this policy will be implemented via iptables on each server.

Note: To block traffic to your public interface, you can either disable your public interface or set up firewall rules to achieve a similar effect with Iptables. We will go with the firewall option because we can configure it block unwanted network traffic, while allowing our server to access the Internet when it initiates the connection (this is useful for things like downloading updates on the server).

How To Set Up a Firewall with UFW on Ubuntu 14.04

05/07/2021 Comments off

Source: DigitalOcean – Mitchell Anicas

Introduction

UFW, or Uncomplicated Firewall, is an interface to iptables that is geared towards simplifying the process of configuring a firewall. While iptables is a solid and flexible tool, it can be difficult for beginners to learn how to use it to properly configure a firewall. If you’re looking to get started securing your network, and you’re not sure which tool to use, UFW may be the right choice for you.

This tutorial will show you how to set up a firewall with UFW on Ubuntu 14.04.

Prerequisites

Before you start using this tutorial, you should have a separate, non-root superuser account—a user with sudo privileges—set up on your Ubuntu server. You can learn how to do this by completing at least steps 1-3 in the Initial Server Setup with Ubuntu 14.04 tutorial.

UFW is installed by default on Ubuntu. If it has been uninstalled for some reason, you can install it with apt-get:

sudo apt-get install ufw

Using IPv6 with UFW

If your Ubuntu server has IPv6 enabled, ensure that UFW is configured to support IPv6 so that it will manage firewall rules for IPv6 in addition to IPv4. To do this, open the UFW configuration with your favorite editor. We’ll use nano:

sudo nano /etc/default/ufw

Then make sure the value of « IPV6 » is to equal « yes ». It should look like this:

/etc/default/ufw excerpt
...
IPV6=yes
...

Save and quit. Hit Ctrl-X to exit the file, then Y to save the changes that you made, then ENTER to confirm the file name.

When UFW is enabled, it will be configured to write both IPv4 and IPv6 firewall rules.

This tutorial is written with IPv4 in mind, but will work fine for IPv6 as long as you enable it.

Check UFW Status and Rules

At any time, you can check the status of UFW with this command:

sudo ufw status verbose

By default, UFW is disabled so you should see something like this:

Output:
Status: inactive

If UFW is active, the output will say that it’s active, and it will list any rules that are set. For example, if the firewall is set to allow SSH (port 22) connections from anywhere, the output might look something like this:

Output:
Status: active
Logging: on (low)
Default: deny (incoming), allow (outgoing), disabled (routed)
New profiles: skip

To                         Action      From
--                         ------      ----
22/tcp                     ALLOW IN    Anywhere

As such, use the status command if you ever need to check how UFW has configured the firewall.

Before enabling UFW, we will want to ensure that your firewall is configured to allow you to connect via SSH. Let’s start with setting the default policies.

Lire la suite…