Archive

Articles taggués ‘DDoS’

Block WordPress xmlprc.php DDOS attacks using Fail2Ban

17/04/2024 Comments off

Few days ago, my friend’s WordPress website went down. After investigation, I have figured out that it was receiving massive amount of posts requests to the xmlrpc.php file, which brings the apache and mysql to eat up all the system resources and the website crashed. Fortunately, I have figured out the way to mitigate this attack using Fail2Ban, which I’ll share in this post.

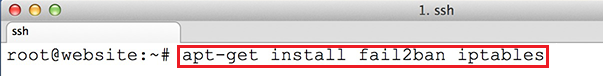
Install the Fail2Ban package using the following command:

apt-get install fail2ban iptables

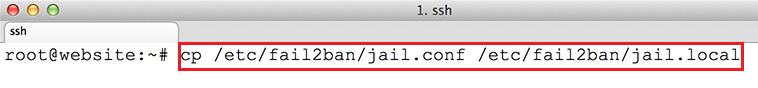
1Make a local copy of jail.conf file for configuration change:

cp /etc/fail2ban/jail.conf /etc/fail2ban/jail.local

2

Lire la suite…

Testing firewall rules with Hping3 – examples

29/03/2024 Comments off

1. Testing ICMP:

In this example hping3 will behave like a normal ping utility, sending ICMP-echo und receiving ICMP-reply

hping3 -1 0daysecurity.com

2. Traceroute using ICMP:

This example is similar to famous utilities like tracert (Windows) or traceroute (Linux) who uses ICMP packets increasing every time in 1 its TTL value.

hping3 --traceroute -V -1 0daysecurity.com

3. Checking port:

Here hping3 will send a SYN packet to a specified port (80 in our example). We can control also from which local port will start the scan (5050).

hping3 -V -S -p 80 -s 5050 0daysecurity.com

Lire la suite…

Categories: Réseau, Sécurité Tags: , , ,

TCP SYN flood DOS attack with hping3

26/03/2024 Comments off

Hping

Wikipedia defines hping as :

hping is a free packet generator and analyzer for the TCP/IP protocol distributed by Salvatore Sanfilippo (also known as Antirez). Hping is one of the de facto tools for security auditing and testing of firewalls and networks, and was used to exploit the idle scan scanning technique (also invented by the hping author), and now implemented in the Nmap Security Scanner. The new version of hping, hping3, is scriptable using the Tcl language and implements an engine for string based, human readable description of TCP/IP packets, so that the programmer can write scripts related to low level TCP/IP packet manipulation and analysis in very short time.

On ubuntu hping can be installed from synaptic manager.

$ sudo apt-get install hping3

Syn flood

To send syn packets use the following command at terminal

$ sudo hping3 -i u1 -S -p 80 192.168.1.1

The above command would send TCP SYN packets to 192.168.1.1
sudo is necessary since the hping3 create raw packets for the task , for raw sockets/packets root privilege is necessary on Linux.

S – indicates SYN flag
p 80 – Target port 80
i u1 – Wait for 1 micro second between each packet

More options

Lire la suite…

Linux Iptables Limit the number of incoming tcp connection / syn-flood attacks

22/03/2024 Comments off

A SYN flood is a form of denial-of-service attack in which an attacker sends a succession of SYN requests to a target’s system. This is a well known type of attack and is generally not effective against modern networks. It works if a server allocates resources after receiving a SYN, but before it has received the ACK.

if Half-open connections bind resources on the server, it may be possible to take up all these resources by flooding the server with SYN messages. Syn flood is common attack and it can be block with following iptables rules:

iptables -A INPUT -p tcp –syn -m limit –limit 1/s –limit-burst 3 -j RETURN

All incoming connection are allowed till limit is reached:

  • –limit 1/s: Maximum average matching rate in seconds
  • –limit-burst 3: Maximum initial number of packets to match

Open our iptables script, add the rules as follows:

# Limit the number of incoming tcp connections
# Interface 0 incoming syn-flood protection
iptables -N syn_flood
iptables -A INPUT -p tcp --syn -j syn_flood
iptables -A syn_flood -m limit --limit 1/s --limit-burst 3 -j RETURN
iptables -A syn_flood -j DROP
#Limiting the incoming icmp ping request:
iptables -A INPUT -p icmp -m limit --limit  1/s --limit-burst 1 -j ACCEPT
iptables -A INPUT -p icmp -m limit --limit 1/s --limit-burst 1 -j LOG --log-prefix PING-DROP:
iptables -A INPUT -p icmp -j DROP
iptables -A OUTPUT -p icmp -j ACCEPT

First rule will accept ping connections to 1 per second, with an initial burst of 1. If this level crossed it will log the packet with PING-DROP in /var/log/message file. Third rule will drop packet if it tries to cross this limit. Fourth and final rule will allow you to use the continue established ping request of existing connection.
Where,

  • ‐‐limit rate: Maximum average matching rate: specified as a number, with an optional ‘/second’, ‘/minute’, ‘/hour’, or ‘/day’ suffix; the default is 3/hour.
  • ‐‐limit‐burst number: Maximum initial number of packets to match: this number gets recharged by one every time the limit specified above is not reached, up to this number; the default is 5.

You need to adjust the –limit-rate and –limit-burst according to your network traffic and requirements.

Let us assume that you need to limit incoming connection to ssh server (port 22) no more than 10 connections in a 10 minute:

iptables -I INPUT -p tcp -s 0/0 -d $SERVER_IP --sport 513:65535 --dport 22 -m state --state NEW,ESTABLISHED -m recent --set -j ACCEPT
iptables -I INPUT -p tcp --dport 22 -m state --state NEW -m recent --update --seconds 600 --hitcount 11 -j DROP
iptables -A OUTPUT -p tcp -s $SERVER_IP -d 0/0 --sport 22 --dport 513:65535 -m state --state ESTABLISHED -j ACCEPT
Categories: Réseau, Sécurité Tags: , ,

Mod_evasive : un module anti-DDoS pour Apache

19/03/2024 Comments off

Source: tux-planet.fr

Mod_evasive est un module Apache pour contrer les attaques DDoS. Celui-ci est par exemple capable de détecter lorsqu’un utilisateur demande un trop grand nombre de pages sur un site web, sur un délai de temps très court. Voici comment l’installer et le configurer pour une utilisation basique.
Lire la suite…