Archive

Articles taggués ‘database’

Linux Security Basics

22/04/2024 Comments off

One of the most daunting prospects of administering your own server on a public network is dealing with your server’s security. While security threats in a networked world are real and it is always important to be mindful of security issues, protecting against possible attacks is often a matter of exercising basic common sense and adhering to some general best practices.

This guide takes a broad overview of common security concerns and provides a number of possible solutions to common security problems. You are encouraged to consider deploying some of these measures to “harden” your server against possible attacks.

It’s important to remember that all of the solutions we present in this document are targeted at specific kinds of attacks, which themselves may be relevant only in specific configurations. Security solutions need to be tailored to the kind of services that you’re providing and the software you’re running, and the decision whether or not to deploy a specific security solution is often a matter of personal discretion and cost-benefit analysis.

Perhaps most importantly, it should be understood that security is a process, not a product (credit to Bruce Schneier.) There is no “magic bullet” set of guidelines that can be followed to ensure the security of any system. Threats are constantly evolving, so vigilance is required on the part of network administrators to prevent unauthorized access to systems.

Keep Systems and Software Up To Date

One of the most significant sources of security vulnerabilities are systems running out of date software with known security holes. Make a point of using your system’s package management tools to keep your software up to date; this will greatly assist in avoiding easily preventable security intrusions.

Running system updates with the package management tool, using apt-get update && apt-get upgrade (for Debian and Ubuntu Systems) or yum update (for CentOS and Fedora systems) is simple and straightforward. This practice ensures that if your distribution maintains active security updates, your system will be guarded against many security holes in commonly used software packages.

System update tools will, however, not keep software up to date that you’ve installed outside of package management. This includes software that you’ve compiled and installed “by hand” (e.g. with ./configure && make && make install) and web-based applications that you’ve installed from a software developer’s site, as is often the case with applications like WordPress and Drupal. Also excluded from protection will be libraries and packages you’ve installed with supplementary package management tools like Ruby’s Gems, Perl’s CPAN tool, Python easy_install, and Haskell Cabal. You will have to manage the process of keeping these files up to date yourself.

The method you use to make sure that your entire system is kept up to date is a matter of personal preference, and depends on the nature of your workflow. We would recommend trying very hard to use the versions of software provided by your operating system or other programming platform-specific package management tools. If you must install from “source,” we would recommend that you save the tarballs and source files for all such software in /src/ or ~/src/ so that you can keep track of what software you’ve installed in this manner. Often, you can remove a manually compiled application by issuing make uninstall in the source repository (directory). Additionally, it may be helpful to maintain a list of manually installed software, with version numbers and download locations. You may also want to investigate packaging your own software so that you can install it with apt, yum or pacman.

Because of the complexity of maintaining software outside of the system’s package management tools we strongly recommend avoiding manually installing software unless absolutely necessary. Your choice in a Linux distribution should be heavily biased by the availability of software in that distro’s repositories for the systems you need to run on your server.
Lire la suite…

Monitor your MySql replication database

26/03/2024 Comments off

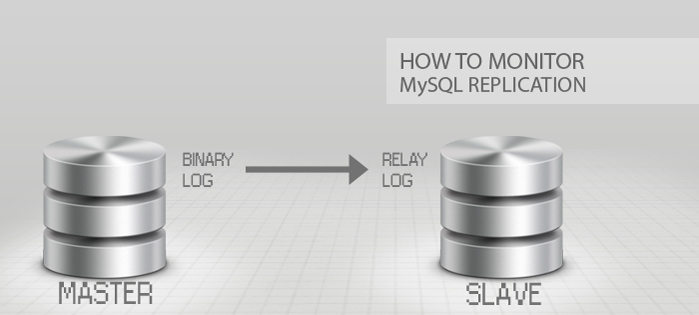
how-to-monitor-mysql-replicationYou have configured your MySql replication, next step is to perform maintenance and monitor your replication. Percona Toolkit for MySQL is a collection of advanced command-line tools to perform a variety of MySQL server and system tasks.
The Percona Toolkit allows you to amongst many tasks to verify MySQL replication integrity, efficiently archive rows, find duplicate indexes, summarize MySQL servers, analyze queries from logs and tcpdump, collect vital system information when problems occur.

To get started you need to install Percona Toolkit, I’m using Ubuntu as an OS on my servers, installing the percona toolkit was straight forward

apt-get install percona-toolkit

To get a summary of your databases use the command – pt-mysql-summary

pt-mysql-summary --u=username --p=password

Next you would want to setup a heartbeat table in your database so you can Monitor MySQL replication delay – for that you will use the pt-heartbeat command.

pt-heartbeat -D wpslavedb --create-table --ask-pass --check --master-server-id 1

You can find the manual for the options here.

pt-heartbeat measures replication lag on a MySQL or PostgreSQL server. You can use it to update a master or monitor a replica. mk-heartbeat depends only on the heartbeat record being replicated to the slave, so it works regardless of the replication mechanism. It works at any depth in the replication hierarchy; for example, it will reliably report how far a slave lags its master’s master’s master.

Start daemonized process to update test.heartbeat table on master:

  pt-heartbeat -D wpslavedb --update -h master-server --daemonize --ask-pass

Monitor replication lag on slave:

  pt-heartbeat -D wpslavedb --monitor -h slave-server --ask-pass
  pt-heartbeat -D wpslavedb --monitor -h slave-server --dbi-driver Pg --ask-pass

Check slave lag once and exit (using optional DSN to specify slave host):

  pt-heartbeat -D wpslavedb --check h=slave-server --ask-pass

If the replication hierarchy is “master -> slave1 -> slave2” with corresponding server IDs 1, 2 and 3, you can:

  pt-heartbeat --daemonize -D wpslavedb --update -h master --ask-pass
  pt-heartbeat --daemonize -D wpslavedb --update -h slave1 --ask-pass

Then check (or monitor) the replication delay from master to slave2:

  pt-heartbeat -D wpslavedb --master-server-id 1 --check slave2 --ask-pass

Or check the replication delay from slave1 to slave2:

  pt-heartbeat -D wpslavedb --master-server-id 2 --check slave2 --ask-pass

if you developing and writing SQL statements, this command is very useful pt-query-digest – Analyze MySQL queries from logs, processlist, and tcpdump

  pt-query-digest slow.log    // requires you to have slow query logged enabled

There are other tools Percona Toolkit, these that I shown is what I find useful for my monitoring and maintenance.

If you want to find out the best MySQL configuration for your application, you can head over to Percona’s website they have a MySql wizards.

Source: torbjornzetterlund.com

Un cluster DRBD / MySQL avec Heartbeat sur Debian 7

25/03/2024 Comments off

Source: denisrosenkranz.com

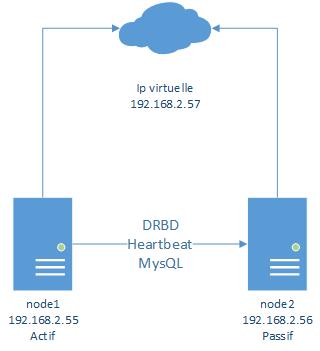
Nous avons vu précédement comment mettre un place un Cluster Apache actif/passif avec DRBD et HeartBeat. Dans ce tutoriel nous allons voir comment faire la même chose mais avec MySQL.

La configuration de DRBD et de Heartbeat est la même que pour le tutoriel précédent.

Voilà ce que nous allons mettre en place

DRBDMySQL

Donc pour faire ce tutoriel suivez le tutoriel suivant jusqu’a « Installation d’apache« :

Un cluster DRBD/Apache avec Heartbeat sur Debian 7

Lire la suite…

Heartbeat/mysql: Bascule esclave/maitre

21/03/2024 Comments off

heartbeat mysqlNous sommes dans la situation où il faut redémarrer le serveur maitre

connection ssh sur les deux serveurs:

sur le maitre
#ssh maitre@IP

Arrêt du service heartbeat sur les deux serveurs

# service heartbeat stop
ou
#/etc/init.d/heartbeat stop

Même chose sur l’esclave
A partir de là, plus personne n’a accès à l’application web

MySql:

on va se placer dans votre homedir sur les deux serveurs.
#cd /home

sur le serveur esclave, on va récupérer la base mysql et la copier sur le serveur maître:

[esclave]# mysqldump -u root -pMDP votre_bdd > votre_bdd.sql
[esclave]# scp votre_bdd.sql maitre@IP:/home

Passons sur le serveur maître:

[maitre]#cd /home

on injecte la base:
[maitre]# mysql -u root -pMDP votre_bdd.sql > votre_bdd.sql

Maintenant, on va activer la réplication de la base MySql du serveur maître sur l’esclave: sur le serveur maître: tout d’abord on va se connecter sur la base

[maitre]# mysql -u root -pMDP

Puis on bloque la base en lecture seule
mysql>: FLUSH TABLES WITH READ LOCK;

On repère la position de la base:

mysql > SHOW MASTER STATUS;
  ------------------ ---------- -------------- -------------------------- 
 | File             | Position | Binlog_Do_DB | Binlog_Ignore_DB         |
  ------------------ ---------- -------------- -------------------------- 
 | mysql-bin.000003 | 73       | test,bar     | foo,manual,mysql         |
  ------------------ ---------- -------------- -------------------------- 
 1 row in set (0.06 sec)

et on note:
mysql-bin.000003 ← le log bin à utiliser
73 ← la position du log
évidemment à adapter suivant le cas.

sur le serveur esclave:
on se connecte aussi à la base mysql
[esclave]# mysql -u root -pMDP

on stoppe la réplication en cours
mysql>stop slave;

on fait une RAZ de la réplication
mysql>reset slave;

On va positionner le serveur esclave comme le maître:
mysql> CHANGE MASTER TO MASTER_HOST = 'IP', MASTER_USER = 'repli', MASTER_PASSWORD = 'repli', MASTER_LOG_FILE = 'mysql-bin.000003', MASTER_LOG_POS = 73;

on démarre la réplication
mysql> start slave;

on vérifie qu’on n’a pas d’erreur

mysql> show slave statusG
 *************************** 1. row ***************************
 Slave_IO_State: Waiting for master to send event
 Master_Host: 10.94.8.58
 Master_User: repli
 Master_Port: 3306
 Connect_Retry: 60
 Master_Log_File: mysql-bin.000003
 Read_Master_Log_Pos: 73
 Relay_Log_File: GLPI_esclave-relay-bin.000024
 Relay_Log_Pos: 660186
 Relay_Master_Log_File: mysql-bin.000003
 Slave_IO_Running: Yes
 Slave_SQL_Running: Yes
 ******
 Last_Errno: 0
 Last_Error:
 ******
 Seconds_Behind_Master: 0
 1 row in set (0.00 sec)

on se déconnecte de mysql
mysql>exit;

sur le serveur maitre on déverrouille l’écriture sur la base
mysql> UNLOCK TABLES;

on se déconnecte de mysql
mysql>exit;

et pour finir on lance le script de lancement automatique des services heartbeat/mon/http/myslq:

[maitre]#./startHA

sur le serveur maitre c’est le même script sauf le service Mon en moins:
[esclave]#./startHA

on vérifie que l’IP virtuel est actif sur le serveur maitre:

[maitre]#ifconfig
eth0:0 Link encap:Ethernet HWaddr 00:22:19:D7:73:48
 inet adr:10.94.8.56 Bcast:10.94.15.255 Masque:255.255.248.0
 UP BROADCAST RUNNING MULTICAST MTU:1492 Metric:1
 Interruption:16

et dans le navigateur firefox, on fait un test de connection:

http://appliweb.com

SI TABLE CRASHED :

d’après le log, on repère la table dite crashed

connexion à mysql :
#mysql -u root -pMDP ;

on sélectionne la base
mysql>use votre_bdd ;

on répare la table
mysql>repair table nomdelatable ;

on sort de mysql
mysql>exit;

PHP MySQL Benchmark Tool (PMBT v. 0.2)

19/02/2024 Comments off

Source: Reasons Unbeknownst

The old saying “Need is the father of innovation” (or something like that) held true this weekend. I was looking for an easy way to benchmark MySQL for some RAM drive InnoDB experimentation but couldn’t find anything cross platform, user friendly, and created after 2005. So I built an early version of what I was looking for.

This is a very synthetic benchmark for now. In some instances InnoDB is much faster than MyISAM (simultaneous reads/writes) but that doesn’t come across in these results. I’m planning on beefing up the benchmark options in later versions. This tool is currently useful in benchmarking hard drive / RAID performance when using InnoDB. It’s also good for basic my.cnf tweaking. Lire la suite…