Les bases de données SQL et plus particulièrement MySQL restent une des pierres angulaires de l’immense majorité des sites internet. MySQL fonctionne très bien out of the box, cependant, dès que la base se trouve assez sollicitée, on s’aperçoit que les réglages par défaut méritent une petite optimisation. Jetons un œil à tout ça !
Récemment, un des serveurs de Peerus commençait à avoir de sacrés pics de load lors des heures de forte charge, avec MySQL pour principal responsable. Une grosse centaine de connexions simultanées et quelques dizaines de requêtes par seconde sur des bases de plusieurs dizaines de giga. C’est un peu plus que le WordPress moyen, mais rien d’ingérable pour un MySQL bien réglé.
Dès lors, avant d’imaginer prendre un serveur plus puissant, sharder les tables ou je ne sais quoi encore, il faut tirer le maximum de notre cher SGBDR. Lire la suite…
Le logiciel pure-ftpd est l’un des serveurs FTP les plus simple à installer et configurer c’est pourquoi si vous cherchez à installer un serveur FTP rapidement sur votre serveur Linux, je ne peux que vous le recommander. Aujourd’hui, nous allons voir comment utiliser pure-ftpd et MySQL simultanément pour permettre la séparation des tâches avec l’enregistrement des comptes utilisateurs dans la base de données et le reste du fonctionnement gérer par pure-ftpd. Le but du tutoriel n’étant pas de vous apprendre à installer et manipuler MySQL, je pars du principe que ce dernier est installé sur la même machine (ou une machine distante) que votre serveur FTP et que vous avez soit MySQL Workbench sous la main ou le client MySQL en ligne de commande pour la partie traitant des manipulations sur la base de donnée.
Installation du serveur Pure-FTPd-mysql
Pour utiliser MySQL avec votre serveur de FTP, il faut que ce dernier ai été compilé avec la commande “–with-mysql“. Heureusement pour nous, plutôt que de ce compliquer la vie à compiler les sources du serveur, nous allons directement installer le paquet tout prêt à l’usage nommé : pure-ftpd-mysql. Même si on vous conseil d’installer “pure-ftpd” ou même qu’on vous demande de le désinstaller si vous l’avez déjà installé, dite oui pour continuer l’installation.
sudo apt install pure-ftpd-mysql
Note : Si vous avez votre serveur FTP déjà en cours de production, l’installation de cette version ne perturbera en rien vos utilisateurs et vous pouvez continuer la suite de ce tutoriel puisque le redémarrage ne sera nécessaire qu’à la fin.
Création de la Base de données
A partir de votre interface PHPMyAdmin ou du client MySQL, vous allez créer un utilisateur ainsi qu’une base de données associés à ce compte.
Création d’un compte utilisateur en requête SQL.
CREATE USER 'pureftpd' identified by 'pwdftp';
Création de la base de donnée et une table qui servira à contenir les comptes utilisateurs.
CREATE DATABASE pureftpd;
Association du compte utilisateur “pureftpd” avec la table “users” en lui attribuant les droits de lecture, écriture, mise à jour et suppression.
GRANT SELECT, INSERT, UPDATE, DELETE ON '*.pureftpd' TO 'pureftpd';
Création de la table où les utilisateurs seront enregistrés.
CREATE TABLE users (
Id int(11) NOT NULL auto_increment PRIMARY KEY,
User varchar(32) NOT NULL default '' UNIQUE KEY,
Password varchar(64) NOT NULL default '',
Uid int(3) NOT NULL default 33,
Gid int(3) NOT NULL default 33,
Dir varchar(255) NOT NULL default '',
QuotaSize int(4) NOT NULL default 250,
ULBandwidth int(2) NOT NULL default 10,
DLBandwidth int(2) NOT NULL default 10
);
If you are running the Apache Web Server or your web hosting provider running Apache based web server, you can use .htaccess configuration file to restrict access to your website. This could be a very important issue from security stand point of view especially if your server is being attacked or hacked from any specific or range of IP addresses.
Now, restricting access method works in two ways. First, you can restrict access to certain IP addresses and allow others. Second, you can restrict access to everyone but few IP addresses only. On this post, I will focus on both method and will try to explain as much as I can.
Restrict Certain IP Addresses
If you want to restrict specific IP addresses from accessing your site, you can use the following lines on your .htaccess file.
order deny,allow
deny from 123.4.5.6
deny from 654.3.2.1
allow from all
These lines above will block “123.4.5.6” and “654.3.2.1” IP addresses from accessing your site. You can add as many IP addresses as you want on this “deny from” list. One interesting fact is, Apache web server gives you lot more flexibility in terms of blocking IP addresses. Take a look at the following lines.
order deny,allow
deny from 123.4.5.
allow from all
If you observe it carefully, you will see that the fourth set of digit is missing on this IP address. It means, if any IP address that matches the first three set of digits will be blocked. So basically anyone with IP address like “123.4.5.1” or “123.4.5.244” won’t be able to access your site as in both IP address matches with the first three (123.4.5.) sets of digits blocked by the Apache web server.
Allow Specific IP Addresses
Think of about a site that you built for a very specific purpose and for very few people, where you do not want everyone to show up. Apache allows you to do that as well.
For an example, lets assume that you built a site that you want one of your friend to be able to access and his IP address is “123.4.5.12”. Simply write the following line on your .htaccess file and you are good to go.
order allow,deny
allow from 123.4.5.12
deny from all
In this case Apache will block all IP addresses except your friends IP address. This is as simple as it can get and I hope you got the basic idea.
Note: On all of my example I used either “allow from all” or “deny from all” at the bottom, this is very important. You must declare either one of these line based on your requirement or things might get little more complicated.
Also remember that all blocked IP addresses would be forwarded or shown an “403 Forbidden” error message. You can definitely customize this message as well but that’s something I will talk about in another post.
Linux operating system and many applications create special files commonly referred to as « logs » to record their operational events. These system logs or application-specific log files are an essential tool when it comes to understanding and troubleshooting the behavior of the operating system and third-party applications. However, log files are not precisely what you would call « light » or « easy » reading, and analyzing raw log files by hand is often time-consuming and tedious. For that reason, any utility that can convert raw log files into a more user-friendly log digest is a great boon for sysadmins.
logwatch is an open-source log parser and analyzer written in Perl, which can parse and convert raw log files into a structured format, making a customizable report based on your use cases and requirements. In logwatch, the focus is on producing more easily consumable log summary, not on real-time log processing and monitoring. As such, logwatch is typically invoked as an automated cron task with desired time and frequency, or manually from the command line whenever log processing is needed. Once a log report is generated, logwatch can email the report to you, save it to a file, or display it on the screen.
A logwatch report is fully customizable in terms of verbosity and processing coverage. The log processing engine of logwatch is extensible, in a sense that if you want to enable logwatch for a new application, you can write a log processing script (in Perl) for the application’s log file, and plug it under logwatch.
One downside of logwatch is that it does not include in its report detailed timestamp information available in original log files. You will only know that a particular event was logged in a requested range of time, and you will have to access original log files to get exact timing information.
Installing Logwatch
On Debian and derivatives:
# aptitude install logwatch
On Red Hat-based distributions:
# yum install logwatch
Configuring Logwatch
During installation, the main configuration file (logwatch.conf) is placed in /etc/logwatch/conf. Configuration options defined in this file override system-wide settings defined in /usr/share/logwatch/default.conf/logwatch.conf.
If logwatch is launched from the command line without any arguments, the custom options defined in /etc/logwatch/conf/logwatch.conf will be used. However, if any command-line arguments are specified with logwatch command, those arguments in turn override any default/custom settings in /etc/logwatch/conf/logwatch.conf.
In this article, we will customize several default settings of logwatch by editing /etc/logwatch/conf/logwatch.conf file.
Detail = <Low, Med, High, or a number>
« Detail » directive controls the verbosity of a logwatch report. It can be a positive integer, or High, Med, Low, which correspond to 10, 5, and 0, respectively.
« MailTo » directive is used if you want to have a logwatch report emailed to you. To send a logwatch report to multiple recipients, you can specify their email addresses separated with a space. To be able to use this directive, however, you will need to configure a local mail transfer agent (MTA) such as sendmail or Postfix on the server where logwatch is running.
Range = <Yesterday|Today|All>
« Range » directive specifies the time duration of a logwatch report. Common values for this directive are Yesterday, Today or All. When « Range = All » is used, « Archive = yes » directive is also needed, so that all archived versions of a given log file (e.g., /var/log/maillog, /var/log/maillog.X, or /var/log/maillog.X.gz) are processed.
Besides such common range values, you can also use more complex range options such as the following.
Range = « 2 hours ago for that hour »
Range = « -5 days »
Range = « between -7 days and -3 days »
Range = « since September 15, 2014 »
Range = « first Friday in October »
Range = « 2014/10/15 12:50:15 for that second »
To be able to use such free-form range examples, you need to install Date::Manip Perl module from CPAN. Refer to this post for CPAN module installation instructions.
Service = <service-name-1>
Service = <service-name-2>
. . .
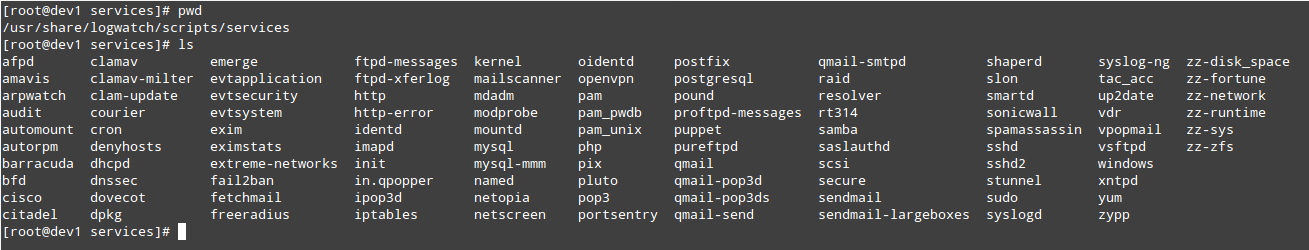
« Service » option specifies one or more services to monitor using logwath. All available services are listed in /usr/share/logwatch/scripts/services, which cover essential system services (e.g., pam, secure, iptables, syslogd), as well as popular application services such as sudo, sshd, http, fail2ban, samba. If you want to add a new service to the list, you will have to write a corresponding log processing Perl script, and place it in this directory.
If this option is used to select specific services, you need to comment out the line « Service = All » in /usr/share/logwatch/default.conf/logwatch.conf.
Format = <text|html>
« Format » directive specifies the format (e.g., text or HTML) of a logwatch report.
Output = <file|mail|stdout>
« Output » directive indicates where a logwatch report should be sent. It can be saved to a file (file), emailed (mail), or shown to screen (stdout).
tcpdump command is also called as packet analyzer.
tcpdump command will work on most flavors of unix operating system. tcpdump allows us to save the packets that are captured, so that we can use it for future analysis. The saved file can be viewed by the same tcpdump command. We can also use open source software like wireshark to read the tcpdump pcap files.
In this tcpdump tutorial, let us discuss some practical examples on how to use the tcpdump command.
1. Capture packets from a particular ethernet interface using tcpdump -i
When you execute tcpdump command without any option, it will capture all the packets flowing through all the interfaces. -i option with tcpdump command, allows you to filter on a particular ethernet interface.
In this example, tcpdump captured all the packets flows in the interface eth1 and displays in the standard output.
Note: Editcap utility is used to select or remove specific packets from dump file and translate them into a given format.
2. Capture only N number of packets using tcpdump -c
When you execute tcpdump command it gives packets until you cancel the tcpdump command. Using -c option you can specify the number of packets to capture.
$ tcpdump -c 2 -i eth0
listening on eth0, link-type EN10MB (Ethernet), capture size 96 bytes
14:38:38.184913 IP valh4.lell.net.ssh > yy.domain.innetbcp.net.11006: P 1457255642:1457255758(116) ack 1561463966 win 63652
14:38:38.690919 IP valh4.lell.net.ssh > yy.domain.innetbcp.net.11006: P 116:232(116) ack 1 win 63652
2 packets captured
13 packets received by filter
0 packets dropped by kernel
The above tcpdump command captured only 2 packets from interface eth0.
Note: Mergecap and TShark: Mergecap is a packet dump combining tool, which will combine multiple dumps into a single dump file. Tshark is a powerful tool to capture network packets, which can be used to analyze the network traffic. It comes with wireshark network analyzer distribution.
3. Display Captured Packets in ASCII using tcpdump -A
The following tcpdump syntax prints the packet in ASCII.
$ tcpdump -A -i eth0
tcpdump: verbose output suppressed, use -v or -vv for full protocol decode
listening on eth0, link-type EN10MB (Ethernet), capture size 96 bytes
14:34:50.913995 IP valh4.lell.net.ssh > yy.domain.innetbcp.net.11006: P 1457239478:1457239594(116) ack 1561461262 win 63652
E.....@.@..]..i...9...*.V...]...P....h....E...>{..U=...g.
......G..7 KA....A...L.
14:34:51.423640 IP valh4.lell.net.ssh > yy.domain.innetbcp.net.11006: P 116:232(116) ack 1 win 63652
E.....@[email protected]...*.V..*]...P....h....7......X..!....Im.S.g.u:*..O&....^#Ba...
E..(R.@.|.....9...i.*...]...V..*P..OWp........
Note:Ifconfig command is used to configure network interfaces