Source: osxdaily.com
Some of the more privacy conscious Mac users out there might put tape over their webcam or use apps like Oversight to detect camera activity. While either of those approaches can be satisfactory for many users (or considered totally paranoid and overboard to others), many advanced Mac users in the security community go a step further and just outright disable their Macs front-facing web camera. This article will show you how to completely deactivate the front FaceTime camera on a Mac.
To be clear, this aims to completely disable the software components behind the built-in camera on Macs which prevents it from being used by any application, this webcam is sometimes called the FaceTime camera or the iSight camera, or simply the front-facing camera. All modern Macs have this camera, it is located at the top of the display and embedded into the screen bezel. By disabling the Macs camera, any application that requires it’s usage will no longer function as intended because camera access will become impossible.
This is an advanced tutorial aimed at advanced users, it is not intended for novice or casual Mac users. This approach disables the Mac built-in camera by changing system level permissions for system level files directly relating to the camera components. If you are not comfortable modifying system files using the command line with super user privileges, do not proceed.
This tutorial applies to modern versions of MacOS including Sierra and El Capitan, you will need turn off rootless temporarily so that you can make modifications to the system folder, if you’re not sure how to do that, you can learn how to disable SIP on Mac OS here. You should aways backup a Mac before making any modifications to system software. Older versions of Mac OS X that wish to disable the iSight camera can follow these instructions instead to accomplish the same effect.
How to Disable the Web Camera on Mac
This is a string of commands that will completely disable the built-in Mac camera, meaning no applications will be able to use the front-facing camera at all. This is intended for advanced users only who thoroughly understand proper syntax and command line usage.
- Back up the Mac if you have not done so already, then you will need to disable SIPfirst (and yes you should re-enable it when finished)
- Open the Terminal app as found in /Applications/Utilities/
- One by one on their own line and executed separately, issue the following five command strings into the command line and authenticate:
sudo chmod a-r /System/Library/Frameworks/CoreMediaIO.framework/Versions/A/Resources/VDC.plugin/Contents/MacOS/VDC
sudo chmod a-r /System/Library/PrivateFrameworks/CoreMediaIOServicesPrivate.framework/Versions/A/Resources/AVC.plugin/Contents/MacOS/AVC
sudo chmod a-r /System/Library/QuickTime/QuickTimeUSBVDCDigitizer.component/Contents/MacOS/QuickTimeUSBVDCDigitizer
sudo chmod a-r /Library/CoreMediaIO/Plug-Ins/DAL/AppleCamera.plugin/Contents/MacOS/AppleCamera
sudo chmod a-r /Library/CoreMediaIO/Plug-Ins/FCP-DAL/AppleCamera.plugin/Contents/MacOS/AppleCamera
- Exit Terminal when complete, don’t forget to re-enable SIP on the Mac as well
(Note you can also use chmod 200 instead of a-r if you prefer using numbers, the effect will be the same and permissions will be –w——-)
After the Mac camera has been disabled this way, if you attempt to open FaceTime, Skype, Photo Booth, QuickTime, iMovie, or any other app which uses the built-in camera, you will get a message stating “there is no connected camera” on the Mac – which is exactly what you would want to see if you disabled the camera intentionally.
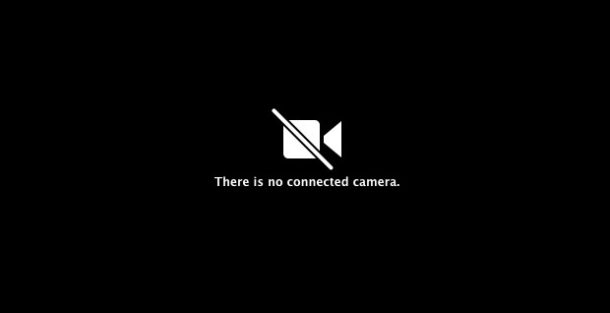
You should not need to reboot for the changes to take effect, though you may need to relaunch some active applications with camera access.
How to Re-Enable the Camera on Mac
Just as before when disabling the camera, to re-enable the Mac camera this way you will likely need to temporarily disable SIP in Mac OS before beginning. Then the commands to issue one by one are as follows:
sudo chmod a+r /System/Library/Frameworks/CoreMediaIO.framework/Versions/A/Resources/VDC.plugin/Contents/MacOS/VDC
sudo chmod a+r /System/Library/PrivateFrameworks/CoreMediaIOServicesPrivate.framework/Versions/A/Resources/AVC.plugin/Contents/MacOS/AVC
sudo chmod a+r /System/Library/QuickTime/QuickTimeUSBVDCDigitizer.component/Contents/MacOS/QuickTimeUSBVDCDigitizer
sudo chmod a+r /Library/CoreMediaIO/Plug-Ins/DAL/AppleCamera.plugin/Contents/MacOS/AppleCamera
sudo chmod a+r /Library/CoreMediaIO/Plug-Ins/FCP-DAL/AppleCamera.plugin/Contents/MacOS/AppleCamera
(Note you can also use chmod 755 instead of a+r if you prefer using numbers to return to -rwxr-xr-x, the effect will be the same)
You’ll notice the difference between the enabling and disabling commands are simply the permissions change chmod command flag – has turned into a +, indicating the file(s) have read access now whereas before they did not, which is what prevented the camera from working.
If this approach is insufficient for your privacy or security needs for whatever reason, you’d likely need to go a step further and actually disassemble your Mac hardware to physically disconnect any camera cables, a task which is quite advanced but undeniably the most effective approach if you want to completely disable the Mac camera and don’t ever want the Macs camera to be used.
Why would I want to disable the Mac camera?
Most Mac users would not want to disable their FaceTime / iSight camera. Typically only very advanced Mac users who have a specific reason to completely disable the built-in camera on their Mac would want to do this, whether they are systems administrators, security professionals, for privacy reasons, or otherwise. This is not intended for the average Mac user. If you’re an average, casual, or novice Mac user who is concerned about privacy and any possible camera shenanigans, try putting tape on your web cam, like the FBI director does, which is much lower tech and less involved, easy to reverse, and quite effective since obviously if something is obstructing the camera lens than it is not usable.
