Source: unixmen.com
Introduction
You have a problem while monitoring your servers, switches or physical machines. Observium fits your need. As a free monitoring system, it helps you to monitor your servers remotely. It is an auto-discovering SNMP based network monitoring platform written in PHP which includes support for a wide range of network hardware and operating systems including Cisco, Windows, Linux, HP, NetApp and many other. I will give you the steps to follow while setting up an Observium server on Ubuntu 12.04.
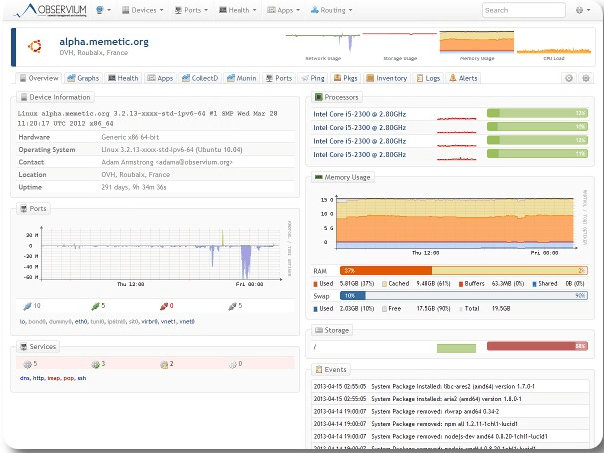
Currently there are two different versions of observium.
- The observium Community is a free tool and licensed under the QPL Open Source license. This version is the best solution for small deployments. It gets security updates each 6 months.
- While the second version, the Observium Professional is distributed under SVN based release mechanism. And it gets daily security updates. This tool is the best for Service Provider and enterprises deployments.
For more information you can visit the offcial website of Observium.
Lire la suite…
1. Testing ICMP:
In this example hping3 will behave like a normal ping utility, sending ICMP-echo und receiving ICMP-reply
hping3 -1 0daysecurity.com
2. Traceroute using ICMP:
This example is similar to famous utilities like tracert (Windows) or traceroute (Linux) who uses ICMP packets increasing every time in 1 its TTL value.
hping3 --traceroute -V -1 0daysecurity.com
3. Checking port:
Here hping3 will send a SYN packet to a specified port (80 in our example). We can control also from which local port will start the scan (5050).
hping3 -V -S -p 80 -s 5050 0daysecurity.com
Lire la suite…
Hping
Wikipedia defines hping as :
hping is a free packet generator and analyzer for the TCP/IP protocol distributed by Salvatore Sanfilippo (also known as Antirez). Hping is one of the de facto tools for security auditing and testing of firewalls and networks, and was used to exploit the idle scan scanning technique (also invented by the hping author), and now implemented in the Nmap Security Scanner. The new version of hping, hping3, is scriptable using the Tcl language and implements an engine for string based, human readable description of TCP/IP packets, so that the programmer can write scripts related to low level TCP/IP packet manipulation and analysis in very short time.
On ubuntu hping can be installed from synaptic manager.
$ sudo apt-get install hping3
Syn flood
To send syn packets use the following command at terminal
$ sudo hping3 -i u1 -S -p 80 192.168.1.1
The above command would send TCP SYN packets to 192.168.1.1
sudo is necessary since the hping3 create raw packets for the task , for raw sockets/packets root privilege is necessary on Linux.
S – indicates SYN flag
p 80 – Target port 80
i u1 – Wait for 1 micro second between each packet
More options
Lire la suite…
Source: nixCraft
Spoofing and bad address attack tries to fool the server and try to claim that packets had come from local address/network.
Following IP/netwok address are know to open this kind of attack:
Incoming source IP address is your servers IP address
Bad incoming address from following ranges:
- 0.0.0.0/8
- 127.0.0.0/8
- 10.0.0.0/8
- 172.16.0.0/12
- 192.168.0.0/16
- 192.168.0.0/16
- 224.0.0.0/3
- Your own internal server/network ip address/ranges.
Lire la suite…