Si vous êtes sous Mac OSX et que vous avez besoin d’un petit serveur HTTP sur le pouce afin de mettre à dispo quelques pages web statiques (pas de PHP, uniquement du HTML), il n’est pas nécessaire d’installer un Nginx ou un Apache. Il suffit d’ouvrir un terminal et d’entrer la commande suivante :
python -m SimpleHTTPServer 8000
Ensuite, avec votre navigateur sur la machine distante, rendez-vous sur http://IP_DE_LA_MACHINE:8000 (ou localhost:8000 si vous êtes en local) et naviguez dans les répertoires jusqu’à atteindre le fichier HTML que vous souhaitez afficher. A noter que vous pouvez changer le port dans la commande.
Rien de sécurisé là-dedans, donc faites attention, mais l’astuce est toujours bonne à connaitre.
cmd + space ===== highlight menu cmd + opt + space ===== highlight window cmd + delete ===== move/go to trash shfit + cmd + delete ===== empty/clean trash shfit + opt + cmd + delete =====force/immediate empty trash cmd + n ===== new finder window shift + cmd + n ===== new folder cmd + tab ===== get/view info opt + cmd + tab ===== show/display inspector cmd + y/space bar ===== quick look cmd + e ===== eject volume cmd + j ===== view options show/display cmd + k ===== server connect shift + cmd + a ===== applications folderopen shift + cmd + c ===== computer folder open cmd + up arrow ===== enclosing folder open cmd + f ===== find/search
key commands-2 (text editing)
cmd + left arrow ===== go/move to start/end line cmd + up arrow ===== go/move to start/end document opt + left arrow ===== go/move to previous/next word opt + up arrow ===== go/move to previous/next paragraph cmd + x ===== cut cmd + c ===== copy cmd + v ===== paste cmd + a ===== select all cmd + l ===== with selection web search cmd + y ===== with selection sticky note
shift + cmd + 3 ===== screen/appear to file shift + ctrl + cmd + 3 ===== screen/appear to clipboard shift + cmd + 4 ===== area to file space to get window shift + ctrl + cmd + 4 ===== area to clipboard space to get window
key commands-5 (mission control)
ctrl + up arrow ===== mission control view/display
ctrl + down arrow ===== appʼs windows show/display f11 ===== desktop show/display f12 ===== dashboard show/display ctrl + left/right arrow ===== between spaces move tab ===== windows show/display for next app then press ctrl + down arrow spacebar ===== window enlarge under cursor then press ctrl + up arrow
key commands-6 (keyboard control focus)
ctrl + f2 ===== menu bar focus ctrl + f3 ===== dock focus ctrl + f5 ===== window toolbar focus ctrl + f8 ===== menu bar status icons focus left, right, up & down arrow ===== navigate (return) esc ===== exit
key commands-7 (switching applications & windows)
cmd + tab ===== advance/go next app cmd + ` ===== current app’s next window opt + cmd + d ===== dock hide/show
cmd + n ===== new window cmd + , ===== app preferences cmd + o ===== open cmd + h ===== app hide cmd + w ===== close opt + cmd + h ===== others hide cmd + s ===== save cmd + t ===== fonts panel show/display shift + cmd + s ===== save as shift + cmd + c ===== colors panel show/display cmd + p ===== print shift + cmd + / ===== help cmd + q ===== quit/exit ctrl + cmd + f ===== full screen mode
key commands-10 (startup keys)
opt ===== boot volume choose opt + cmd + p + r ===== reset pram cmd + s ===== boot single user mode cmd + r ===== internet & disk utility recovery cmd + t ===== go into target disk mode
monit is a utility for managing and monitoring, processes, files, directories and devices on a UNIX system. Monit conducts automatic maintenance and repair and can execute meaningful causal actions in error situations.
Monit Features
Daemon mode – poll programs at a specified interval
Monitoring modes – active, passive or manual
Start, stop and restart of programs
Group and manage groups of programs
Process dependency definition
Logging to syslog or own logfile
Configuration – comprehensive controlfile
Runtime and TCP/IP port checking (tcp and udp)
SSL support for port checking
Unix domain socket checking
Process status and process timeout
Process cpu usage
Process memory usage
Process zombie check
Check the systems load average
Check a file or directory timestamp
Alert, stop or restart a process based on its characteristics
MD5 checksum for programs started and stopped by monit
Alert notification for program timeout, restart, checksum, stop resource and timestamp error
Firewalls are heavily used to secure private networks (home or corporate). Usually, they are used to protect the network from:
intrusions from outsiders
misuse from insiders
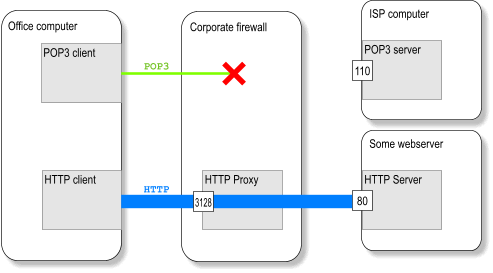
In a TCP/IP environment, the typical corporate firewall configuration is to block everything (both incoming and outgoing), and give access to the internet only through a HTTP proxy. The proxy usually has filtering capabilities (censors URLs and file types), and access to the proxy often requires credentials (login/password). This gives greater contol to the network administrator over what and who is going in and out of the network.
Still, this should not considered a ultimate weapon, and network administrators should not rely on the firewalls only.
Encapsulation is the basis of networking. For example, HTTP is encapsulated by TCP, TCP is encapsulated by IP, and IP is often encapsulated in PPP or Ethernet. Encapsulating protocols in an unsual way is often reffered as tunnelling.
As soon as you let a single protocol out, tunelling allows to let anything go through this protocol, and thus through the firewall.
This paper demonstrates how to encapsulate any TCP-based protocol (SMTP, POP3, NNTP, telnet…) into HTTP, thus bypassing the firewall protection/censorship (depending on your point of view)
A word of warning:
In many countries and corporate environments, bypassing a firewall is forbidden and exposes you to sanctions, redundancy, legal proceedings and – in some countries – death penalty. You are warned.
Nevertheless, in some countries this kind of firewall/proxy bypassing is the only way to ensure free speech (such as China or United Arab Emirates where the government severly censors the internet and where firewall bypassing is a national sport.)
Now you known what you’re doing, let’s move on.
The problem
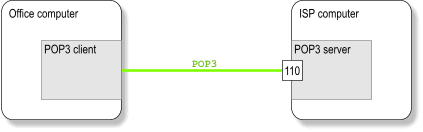
Say you want to fetch your mail from your ISP mail server. You usually simply connect to port 110 on the POP server of your ISP.
Trouble: there is a Big Bad firewall which blocks everything.
Well… it does not exactly block everything: it lets HTTP out through a proxy. Let’s encapsulate our POP3 connection into HTTP.
The tools
We need:
A computer on the internet which has unrestricted access to the internet, such as a home ADSL computer.
SSH is a secure shell (http://www.openssh.com). It provides secure (and compressed) channels between two hosts using SSL. Besides providing a shell (like telnet), it also provides file copy (scp) and TCP port forwarding (tunnelling). We will use the port forwarding feature.
Why not use GNU HTTP Tunnel alone ?
In principle, only HTTP Tunnel is necessary. But this is not desirable:
the tunnel is public: anyone can use your tunnel. Your could be held liable for what anybody has done with your tunnel.
the tunnel is cleartext: anyone can spy on your connection. Your passwords (SMTP, POP3, telnet…) are transmitted in clear text.
the tunnel is not protected: anyone can alter the datastream.
you have to run a new instance of the HTTP Tunnel client and the server for each new tunnel you want to set up.
This is where ssh come in. ssh provides:
authentication (only authorised users can use the tunnel)
privacy (no one can spy on what’s going through the tunnel)
integrity (no one can tamper data going through the tunnel)
easy tunnel set-up (you can create a new tunnel with a single ssh command on the client side).
These tools are available on Unix/Linux and Windows environments.
The whole chain
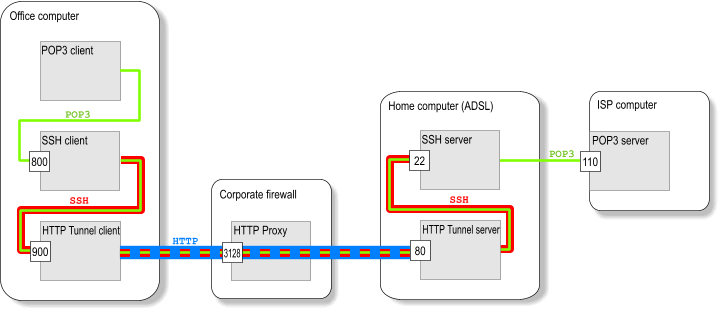
Let’s see how this works. Here is the full chain:
Technically speaking, once this chain is established, connecting to OfficeComputer:800 is identical to connecting to pop3server:110. The mail client will not see the difference.
On the office computer:
TCP data sent to port 800 is encrypted by ssh, which forwards data to port 900.
ssh stream sent to port 900 is chunked in individual HTTP requests by the HTTP Tunnel client and sent to the home computer through the proxy.
On the home computer:
the HTTP Tunnel server receives HTTP requests, decapsulates and re-assembles the ssh stream and forwards it to port 22 (to the ssh server).
the ssh server decrypts the datastream and forwards it to the pop3server on port 110.
As TCP is a bi-directionnaly datastream, once established, the TCP connection can pass data back and forth through the HTTP proxy.
Launchpad is OS X 10.7′s iOS-like app launcher, it’s a nice utility but it does have some quirky behavior in Lion. One of the major issues is that sometimes apps won’t appear in Launchpad at all, or when you delete an app it doesn’t disappear as it’s supposed to. If you run into this, try this tipleft in the comments about LaunchPad Control about refreshing Launchpad and its contents.
Relaunching Launchpad
Launchpad is attached to the Dock app, so the easiest way to relaunch LaunchPad is to kill the Dock from the command line:
killall Dock
Both the Dock and Launchpad will relaunch and that should clear up most minor issues with app persistence.
Refresh Launchpad Contents
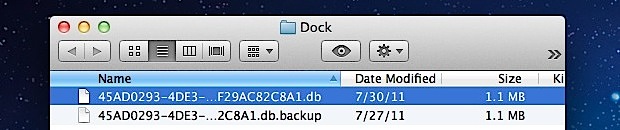
If relaunching alone hasn’t fixed LaunchPad and apps are still not showing up, try deleting Launchpads database files located inside your home ~/Library directory, which forces them to rebuild. The directory path you are looking for is:
~/Library/Application Support/Dock/
The fastest way to get there is by using Command+Shift+G in the Finder to access the “Go To Folder” function, then just paste that directory path in. You will see a folder like this:
If you want to back these up you can, otherwise just delete them by dragging the .db files to the Trash, and then kill the Dock again from the Terminal to force the databases to regenerate.
killall Dock
Take note that you will lose any custom icon placement and folders that are setup within Launchpad, because that information is stored in the database file you are trashing.
One-Line Terminal Command to Refresh Launchpad Contents
If you are comfortable with the command line, you can also do this entire process through the Terminal with the following commands:
rm ~/Library/Application\ Support/Dock/*.db ; killall Dock
If you want control over exactly what shows up in Launchpad rather than just creating a bunch of folders, use the third party System Preference Launchpad Control, it’s free and works as a sql frontend to the Launchpad database.