Archive

Articles taggués ‘DDoS’

Linux Iptables To Block Different Attacks

09/05/2024 Comments off

Source: linoxide.com

Iptables is a Linux kernel based packet filter firewall. The iptables modules are present in the kernel itself, there is no separate daemon for it. This makes it very fast and effective firewall. The iptables rules control the incoming and outgoing traffic on a network device. In this article, we will discuss about some common network attacks, and how we can block them using iptables. Some of the common network attacks are SYN flood attack, smurf attack, land attack, attacks by malfunctioning ICMP packet, and some other forms of DOS attack. Before going into the details of these attacks, let’s have an overview of iptables, and how to use this command.

Iptables

iptables has 3 filtering points for the default table: INPUT, OUTPUT and FORWARD. These are called chains in iptables. As their names suggest, they specify whether a packets is destined for the system (INPUT), originating from it (OUTPUT) or is routed to another node in the network (FORWARD).
The rules in iptables are stored in the form of records in a table. To list the rules, run “iptables -L”

root@local:~# iptables -L
 Chain INPUT (policy ACCEPT)
 target prot opt source destination

 Chain FORWARD (policy ACCEPT)
 target prot opt source destination

 Chain OUTPUT (policy ACCEPT)
 target prot opt source destination

Here, no rules are present for any chain.These rules are read from top to bottom, and if a match occurs, no further rules are checked. So if one rule overwrites any previous rule, then it must be below that rule. So we will append the rules below existing rules. But if your requirement is to insert explicitly, then you can insert them as well.

To insert a rule (above all other rules or at a specified number), -i, and to append, -A option is used. We need to specify the chain, for which we wish to write the rule. The -j option specifies the target, i.e. what we want to do with the packet if a rule is matched. Some of the values are ACCEPT, DROP (or REJECT), RETURN etc. This target can be some other existing or user defined chain. But for the purpose of this article, we will confine ourselves to existing chains only, and will not go in further details.
Lire la suite…

What Is SYN Flood Attack? Detection & Prevention In Linux

09/05/2024 Comments off

Source: linoxide.com

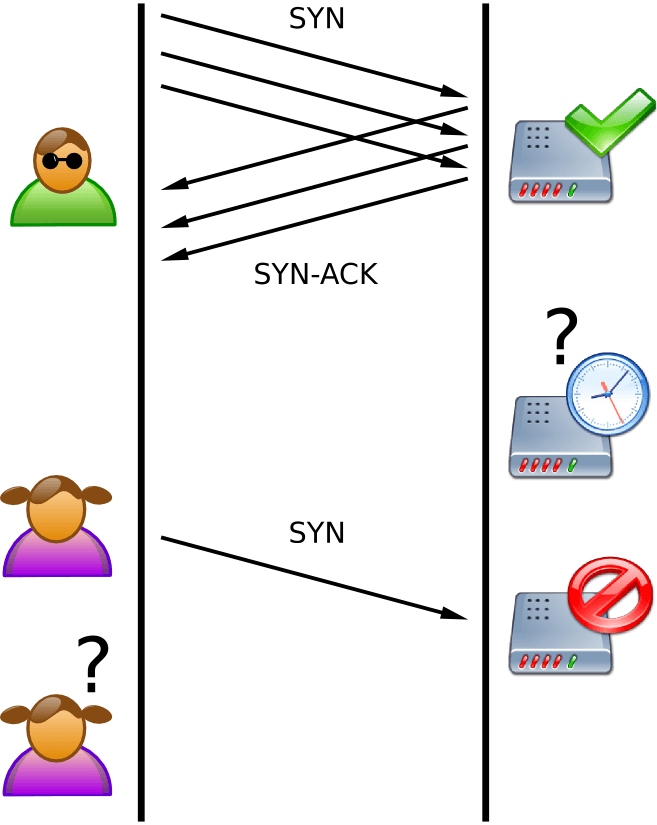
A SYN flood attack is a form of denial-of-service attack in which an attacker sends a large number of SYN requests to a target system’s services that uses TCP protocol. This will consume the server resources to make the system unresponsive to legitimate traffic. This attack can occur on any services that use TCP protocol and mainly on web service. In this article, we will go through the basics of SYN flood attacks and the mitigation steps in detail.

The SYN Flood attack exploits an implementation characteristic of the Transmission Control Protocol (TCP), which is called 3-way handshake. Following are the steps that happen in a normal 3-way handshake.

1. The client requests a connection by sending a SYN (synchronize) message to the server.
2. The server acknowledges this request by sending SYN-ACK back to the client.
3. The client responds with an ACK, and the connection is established

tcp_synflood

A SYN flood attack works by not responding to the server with the expected ACK code. By these half-open connections, the target machines TCP backlog will get filled up and hence all new connections may get ignored. This will cause the legitimate users will also get ignored.

Lire la suite…

DDoS Protection Script For iptables

06/05/2024 Comments off

Source: Digital Point

After a few days of being attacked by a 25,000 zombie botnet, believe me i have tried almost everything possible to make it stop. The best thing that helped was this script, thought it could help here when it’s your turn getting those script-kiddies attackers visiting your servers.

#!/bin/sh
#------------------------------------------------------------------------------
#
# File: SIG-antiDDoS.sh
#
# Compiler: Ruslan Abuzant <[email protected]>
#           PS> Collected From Lots Of Sources
#           PS> Credits: Real Authors (no idea)
#
# URL: http://www.liteforex.org/
#
# License: GNU GPL (version 2, or any later version).
#
# Configuration.
#------------------------------------------------------------------------------

# For debugging use iptables -v.
IPTABLES="/sbin/iptables"
IP6TABLES="/sbin/ip6tables"
MODPROBE="/sbin/modprobe"
RMMOD="/sbin/rmmod"
ARP="/usr/sbin/arp"


# Logging options.
#------------------------------------------------------------------------------
LOG="LOG --log-level debug --log-tcp-sequence --log-tcp-options"
LOG="$LOG --log-ip-options"


# Defaults for rate limiting
#------------------------------------------------------------------------------
RLIMIT="-m limit --limit 3/s --limit-burst 8"

Lire la suite…

Categories: Réseau, Sécurité Tags: , ,

How to stop Small DDOS attacks

06/05/2024 Comments off

dosNodaways seems that every script kid is able to produce a soft DDOS attack, happily they are small and limited so they cant saturate your DNS unless they really know what they are doing.
This is a more or less step by step guide intended for begginers to help stabilize the linux server and prevent further attacks.

There are some basic settings you should have already implemented in your linux server as part of security 101 but this is not always the case and also it is not enough.

Questions and Answers:

  • Limiting the ammount of concurrent connections from the same IP address to your Server.
  • Identifying the offending IP.
  • And kill the Ongoing TCP Connections with TCPKILL.
  • Or use Cutter to kill the connections on any port/Network interface.
  • Drop it With Iptables.
  • Make the DROP Persistant after a reboot. (iptables save and restore)
  • Basic Iptables-save trouble shoot.
  • Stop Start Iptables

This article assumes you have root access to your linux BOX / Server, the IP addresses shown in this guide are randomly generated and in no case are offending connections.

Lire la suite…

Fragmented IP packet forwarding

05/05/2024 Comments off

About Fragmented IP packet forwarding.

I couldn’t really find a suitable topic for this post actually but I will try to find answers for the following questions:

  • How can we fragment an IP packet manually in scapy
  • How does a fragmented packet look like and how the transport layer (TCP/UDP) header is located
  • How do we forward fragmented packets, do we reassemle them?
  • If we don’t reassemble, can we force reassembly?

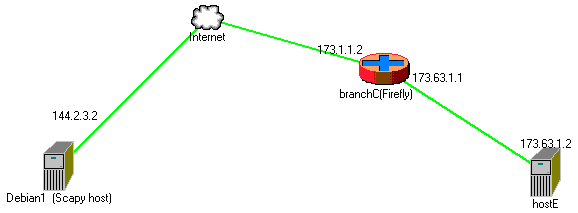
First of all a bit of a theory: if an incoming IP packet is to be forwarded to another next hop and the MTU of this new path is smaller than the packet to be transmitted, we must find a way to forward the packet. If the packet has DF (Don’t Fragment) bit on i.e we are instructed not to fragment the packet most probably by the source, then normally we are expected to send an ICMP packet with type “Fragmentation needed” and pray that on the way back to the source no devices block all ICMP type of traffic. Second scenario is that what if the source lets us fragment the packet. Then we need to fragment it and story from now on is about this part of the scenario and the topology we will use is something like below.

fragmented_packets


Scapy is a fantastic tool to generate your own packets. It is exremely flexible and in our example, we will perform the fragmentation of a packet via our script.

Lire la suite…

Categories: Réseau, Sécurité Tags: , , ,